 Agent Fleet
Self-hosted · Open source (Apache-2.0)
Don't replace your coding agents. Operate them.
Agent Fleet is not another agent framework. It runs the coding-agent CLIs your team already uses, unchanged, on your own servers, and takes on everything around them: isolated workspaces, real git worktrees, and one console to start, follow, steer and account for every session.
Runs today
- Claude Code
- Codex CLI
- GitHub Copilot CLI
- Antigravity CLI
- Cursor CLI
- Kiro
- OpenCode
- Muse Code
- llama.cpp
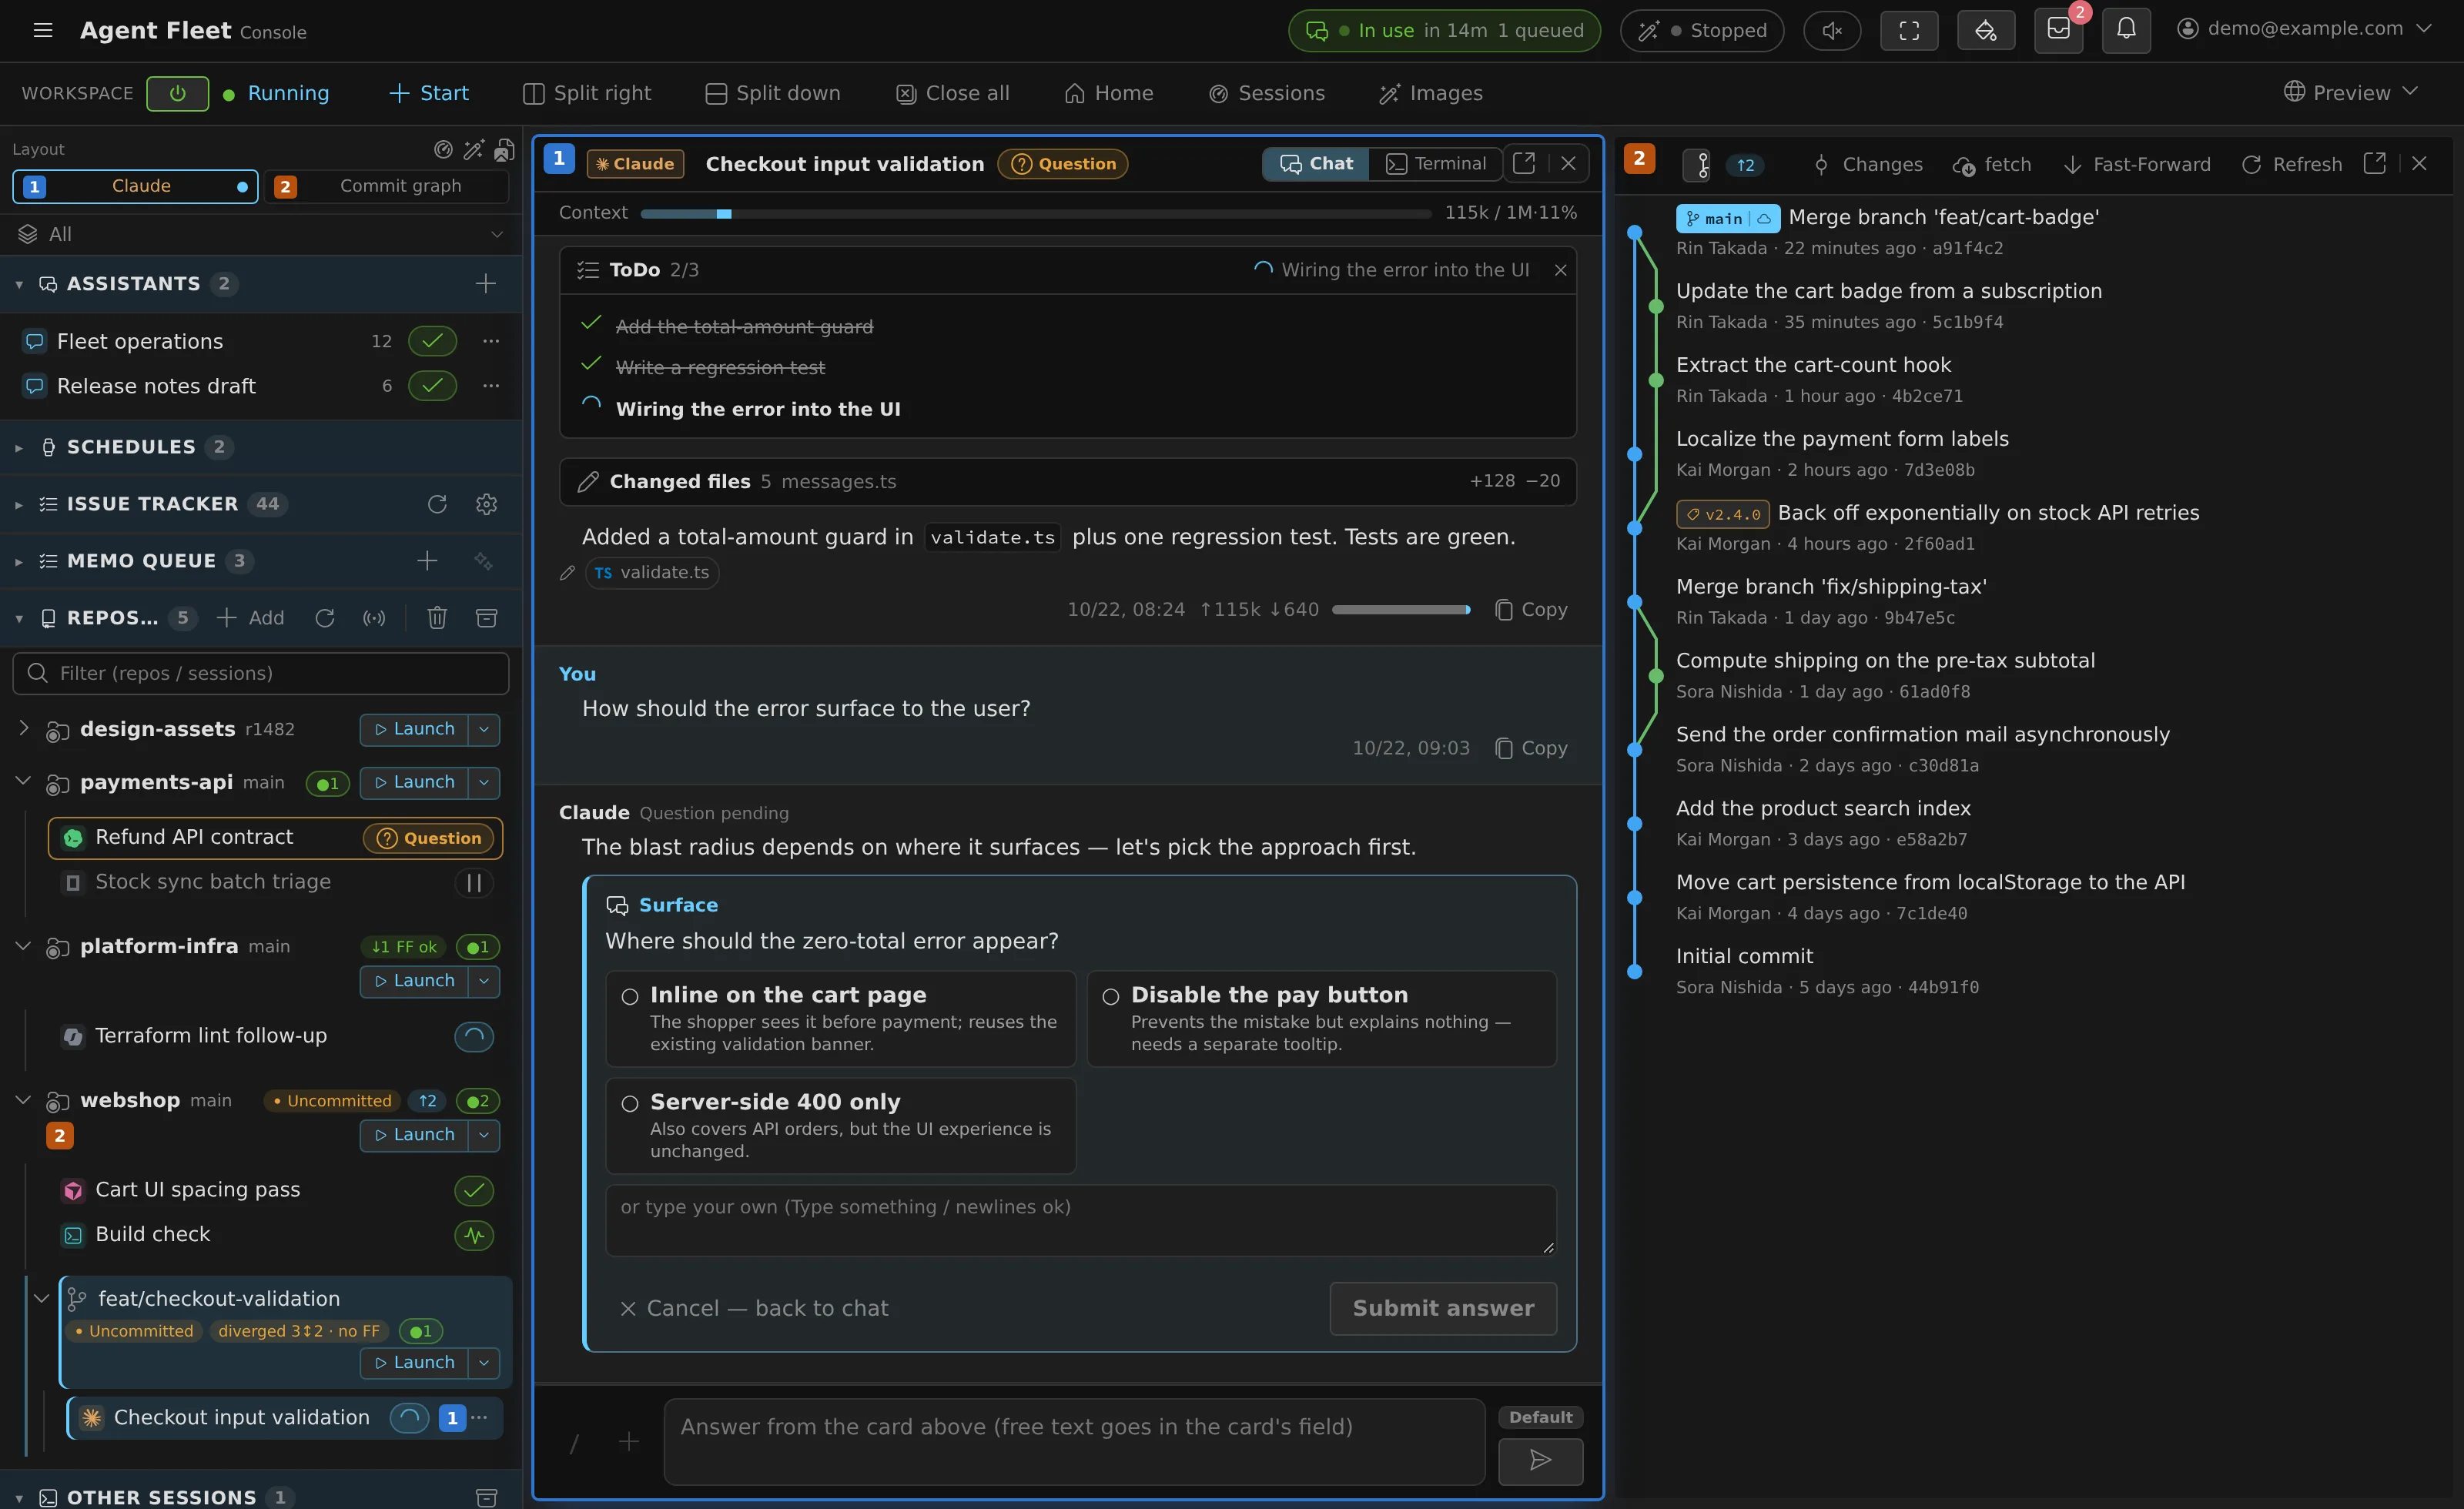
The agents stay. The operations move to one place.
Your agents, as they are
Claude Code stays Claude Code and Codex stays Codex. Each CLI keeps its own sign-in, models and behaviour, so your team keeps the tools it already trusts. Nine of them run side by side.
Work that doesn't wait for you
Sessions run on the server, each in its own git worktree. Close your laptop: questions and permission requests reach you in the browser, on your phone, or in the session's Slack or Discord thread.
Inside your company
One company runs one deployment on its own infrastructure, so credentials, source and conversations stay inside it. The code is open, so you can audit the encryption and the isolation yourself.
A day with Agent Fleet
Hand work off in the morning. It keeps going through the night.
Daytime
- Hand off two issues
One goes to Claude Code and the other to Codex, each in its own git worktree.
- Close the laptop
Both sessions keep working on the server after you leave.
- Answer from your phone
One asks for permission. The request arrives in that session's Slack thread, and you answer it there.
- Review at a desk
The session list shows which finished and which wait on you; each worktree's changes are a click away.
Overnight
- Leave the night shift a job
Tell the assistant in plain words: "every night at 2:00, update the dependencies and run the tests."
- It runs while you sleep
The schedule wakes the stopped workspace, starts the session and runs the prompt.
- A limit doesn't end the night
If a usage limit cuts a Claude Code turn short, the turn picks up on its own when the limit lifts.
- The results are waiting
Each run is in the schedule's history, one click from the session it drove.
Fleet operations
Operate a fleet, not a single chat
What changes when a team runs many agent sessions at once, and what Agent Fleet takes care of.
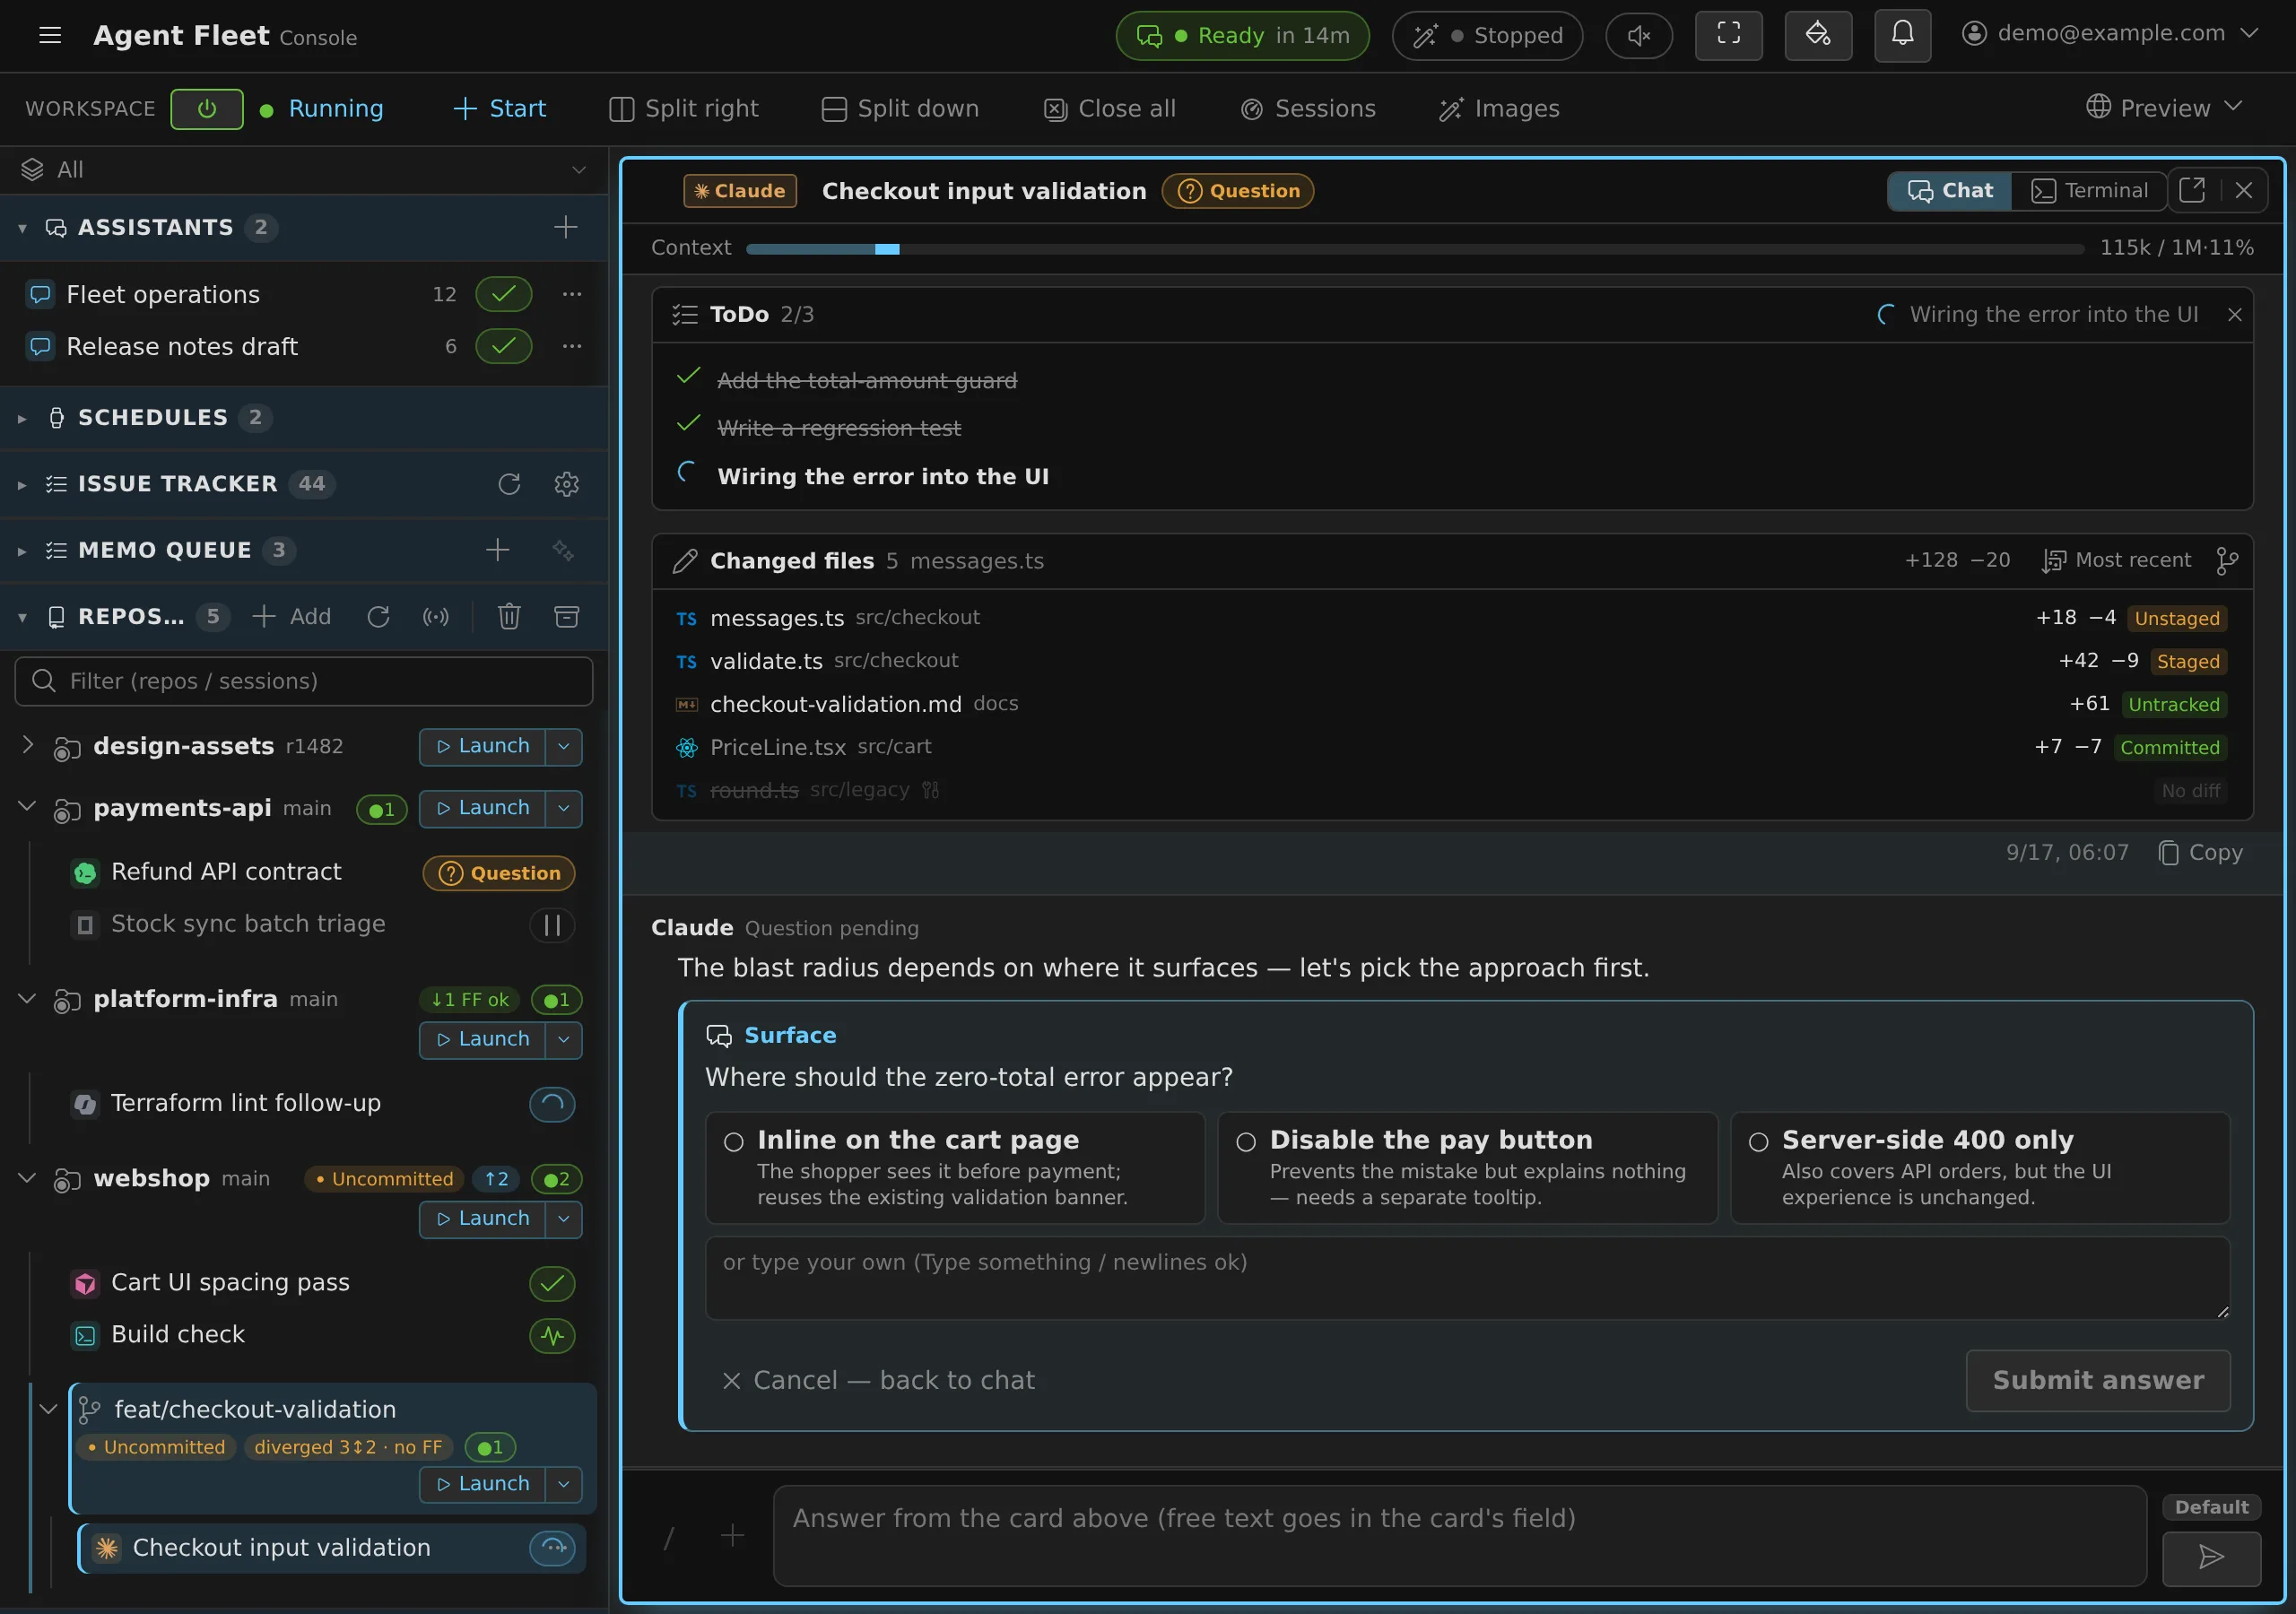
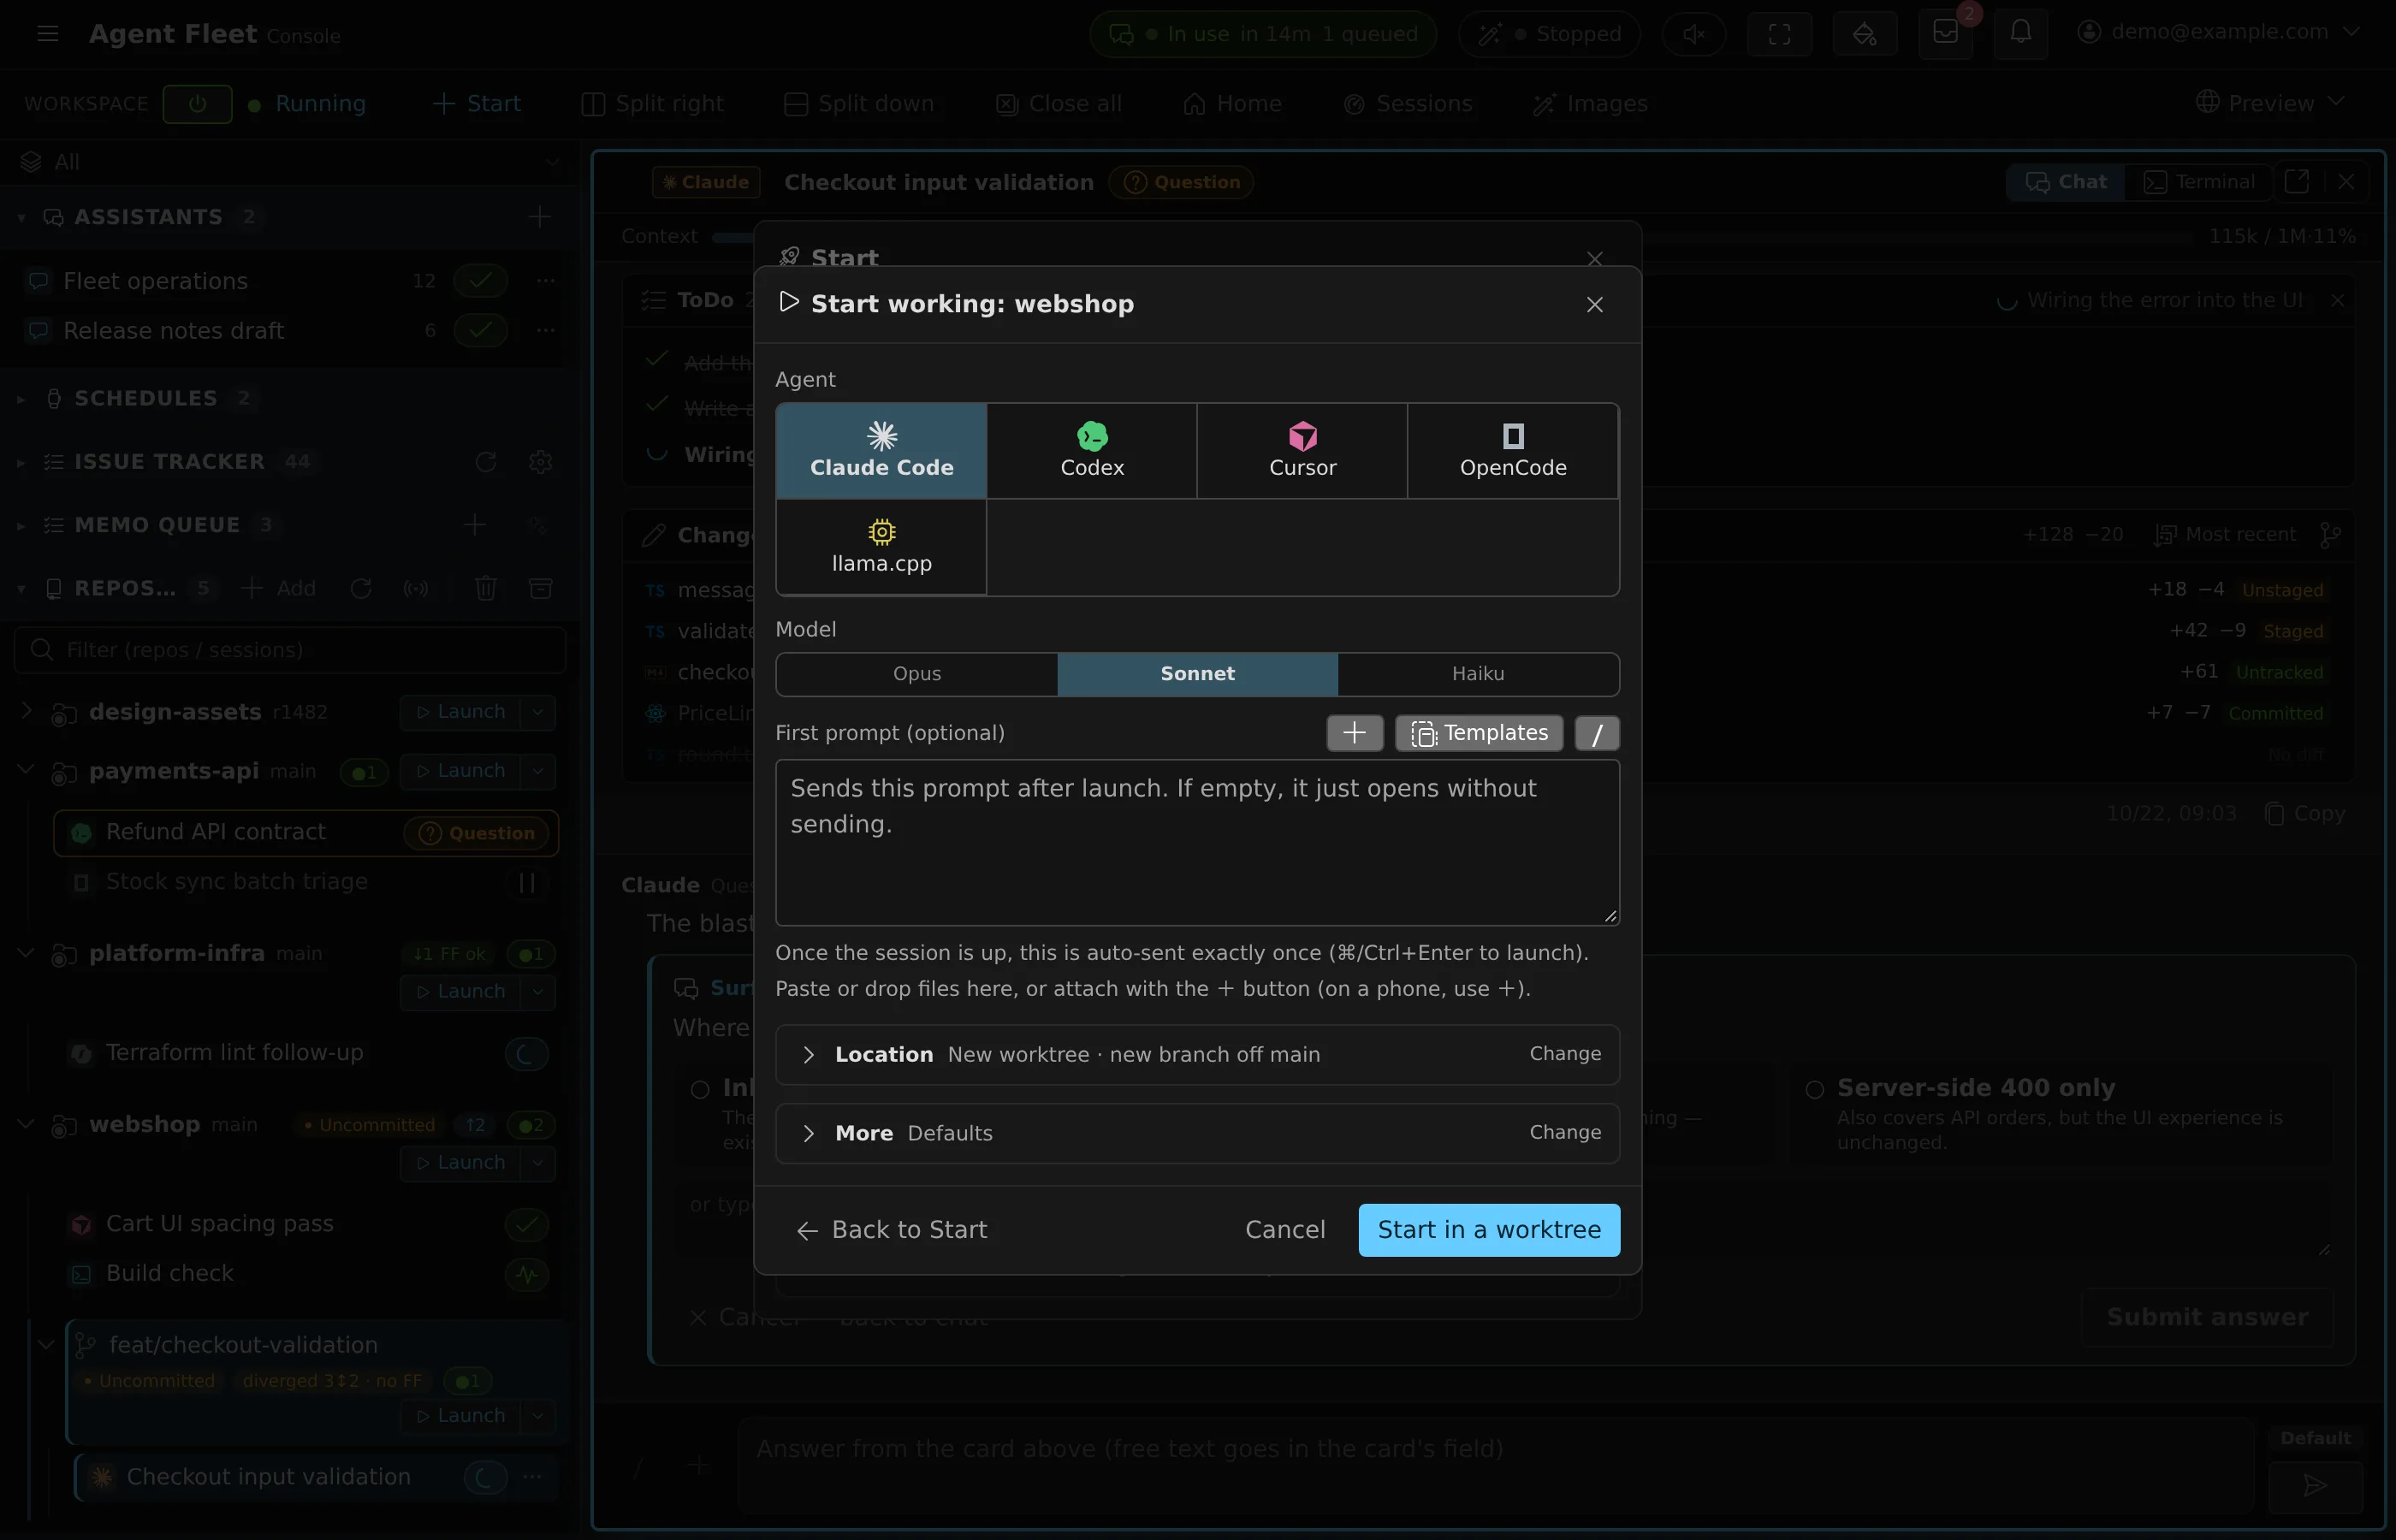
Many sessions at once
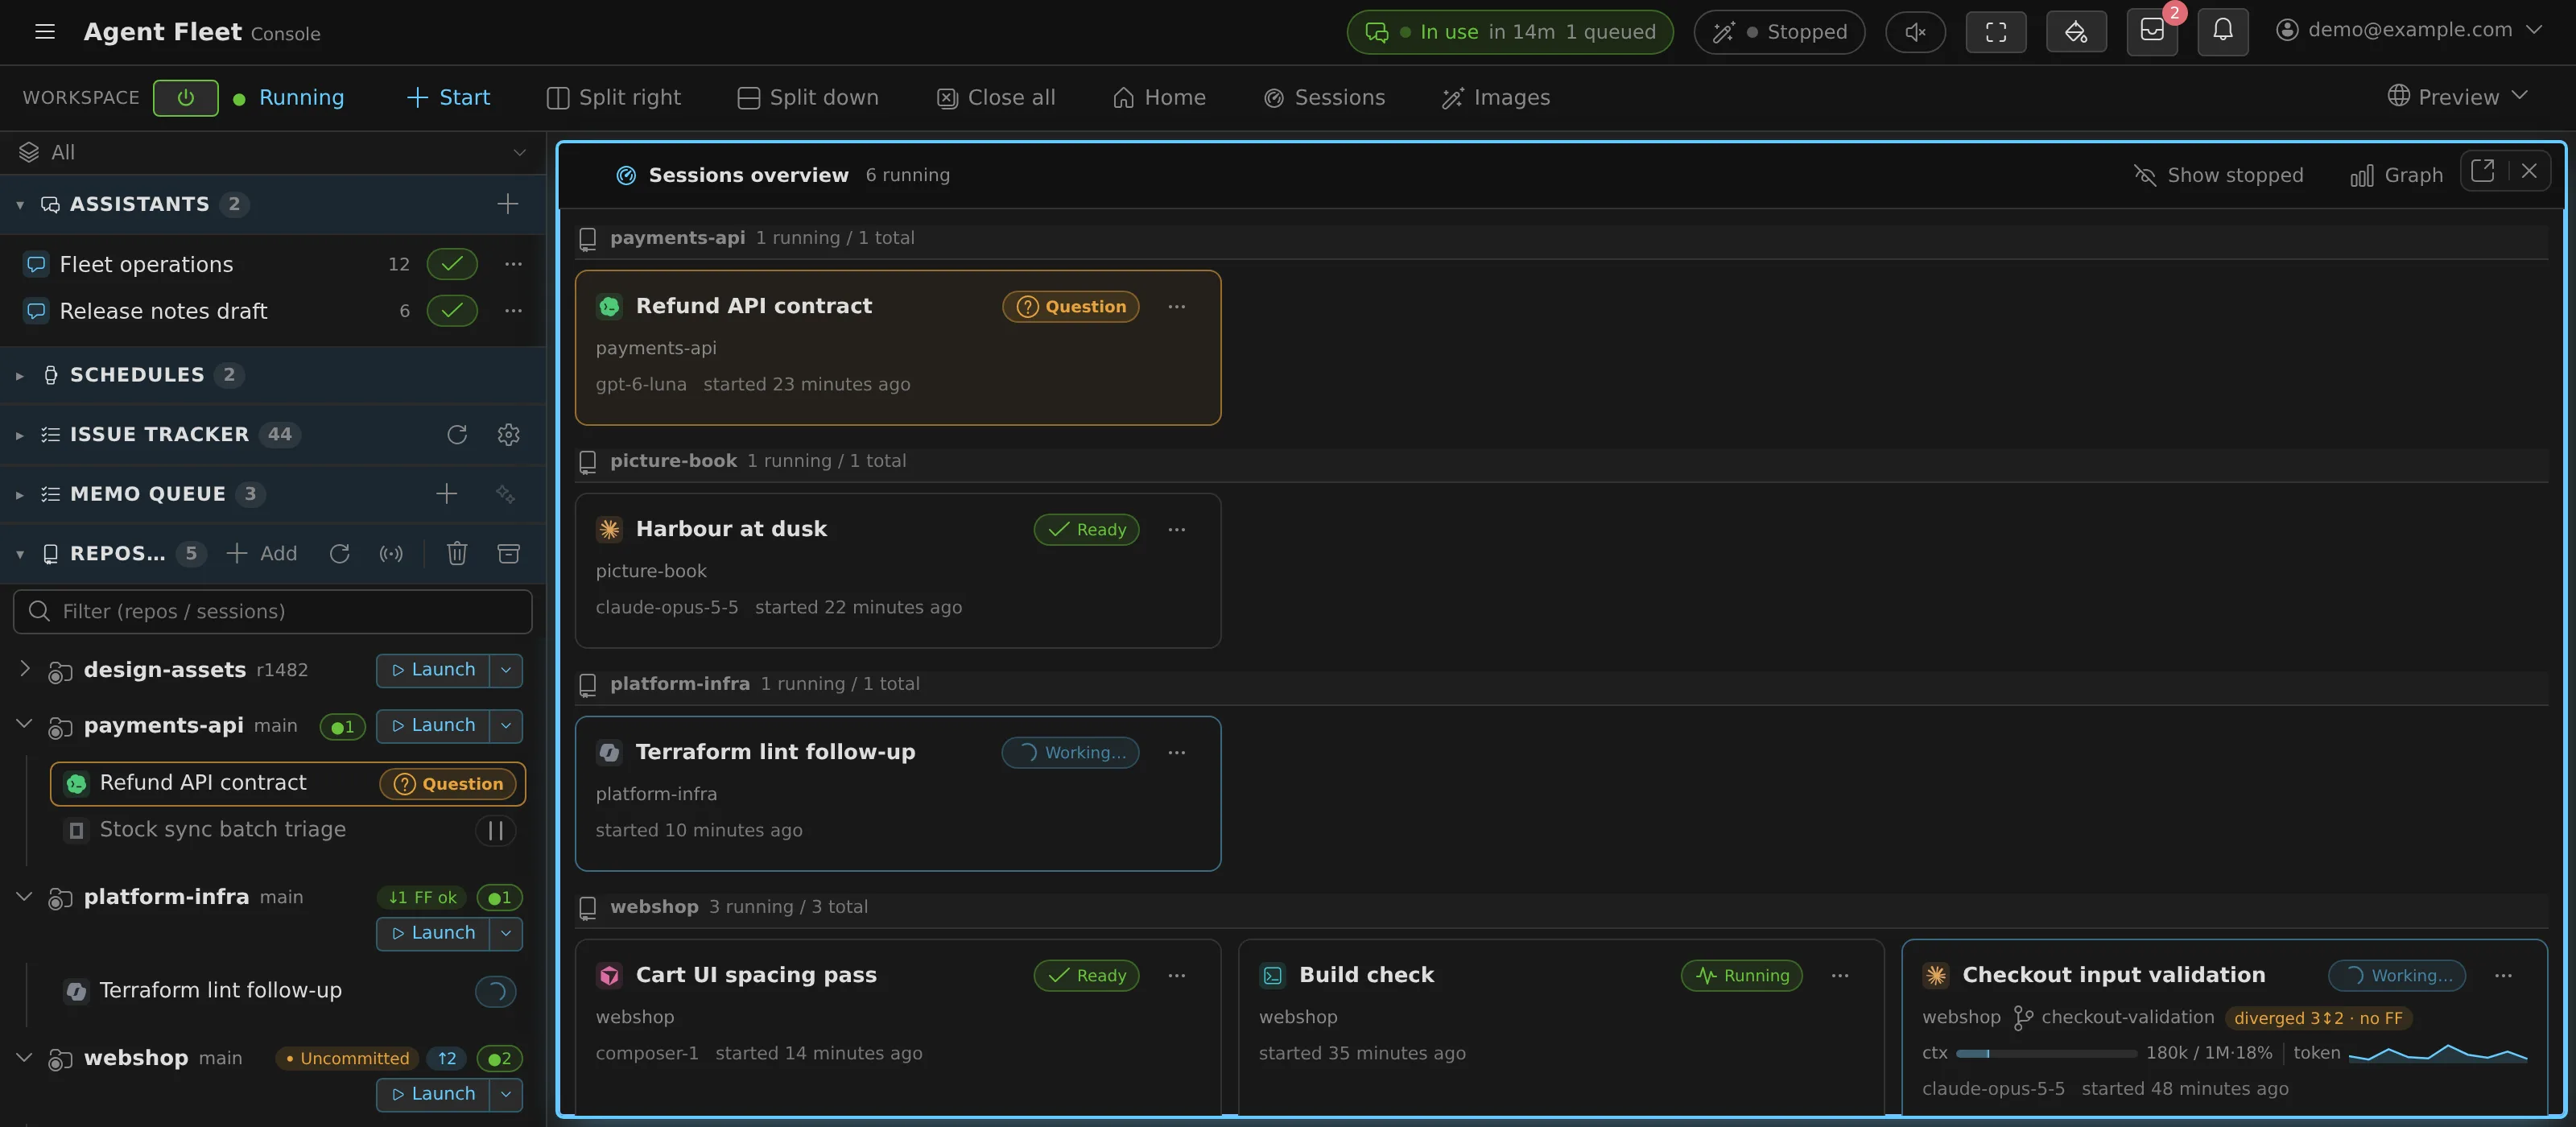
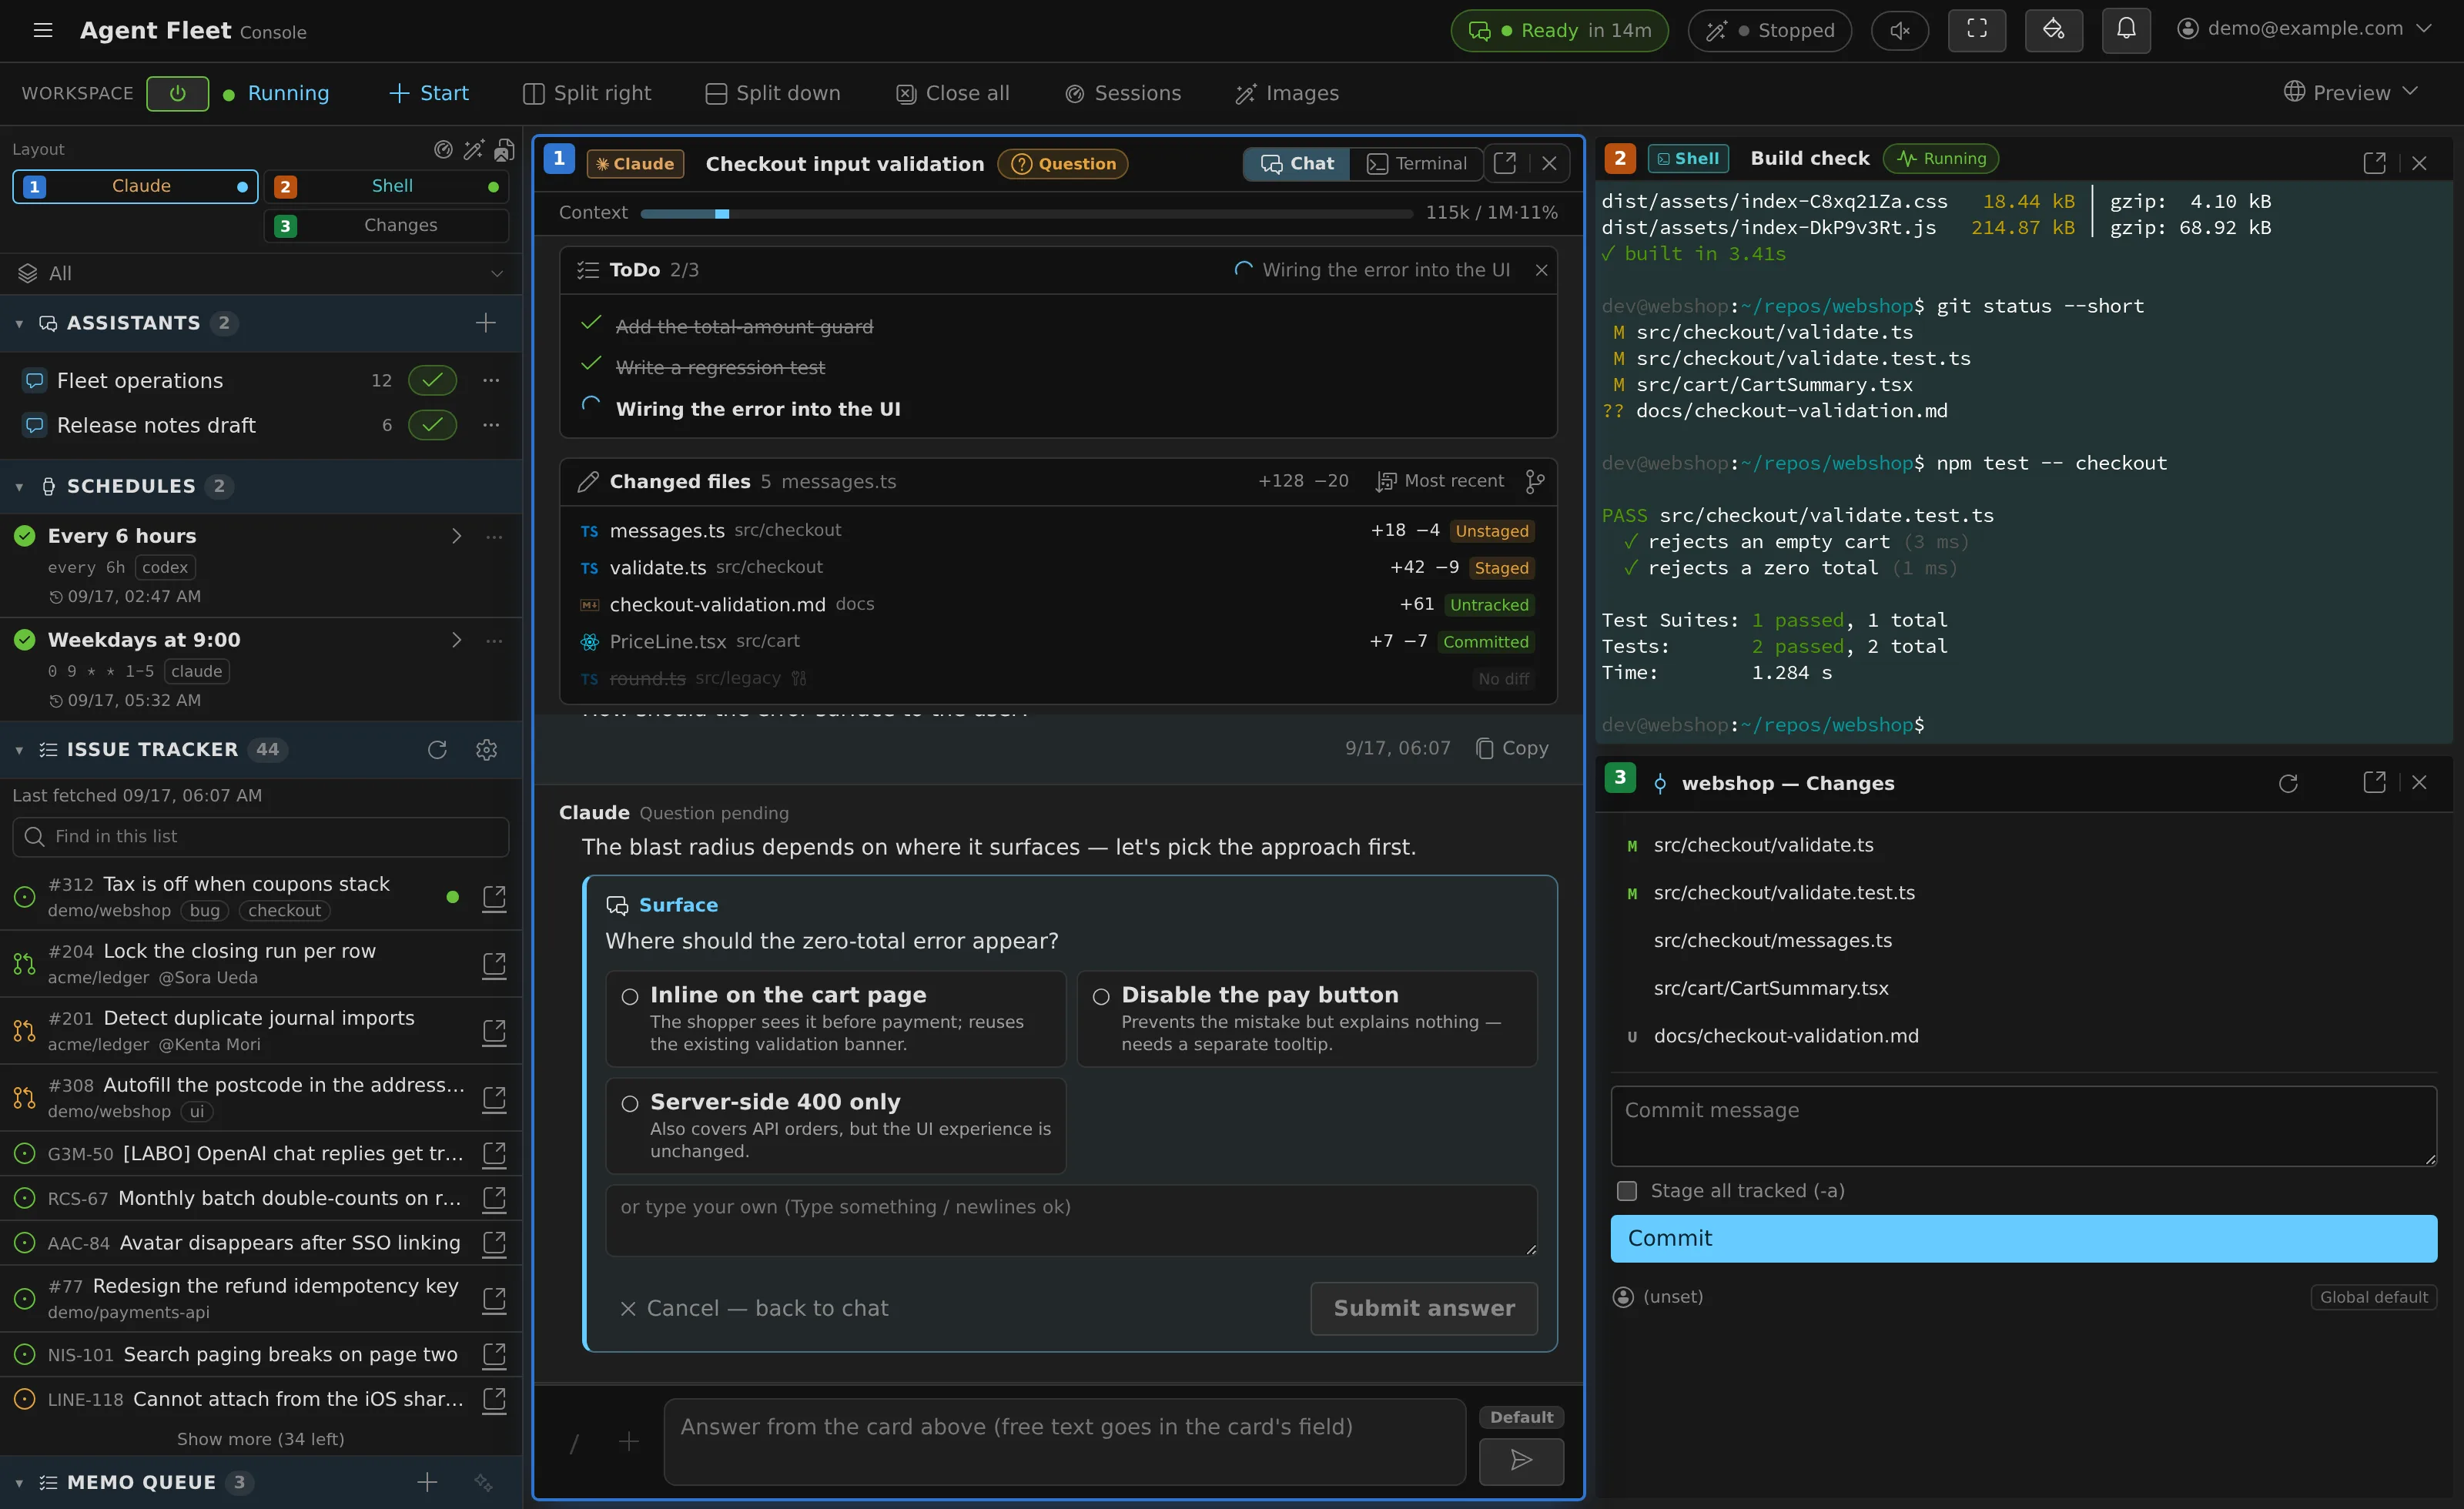
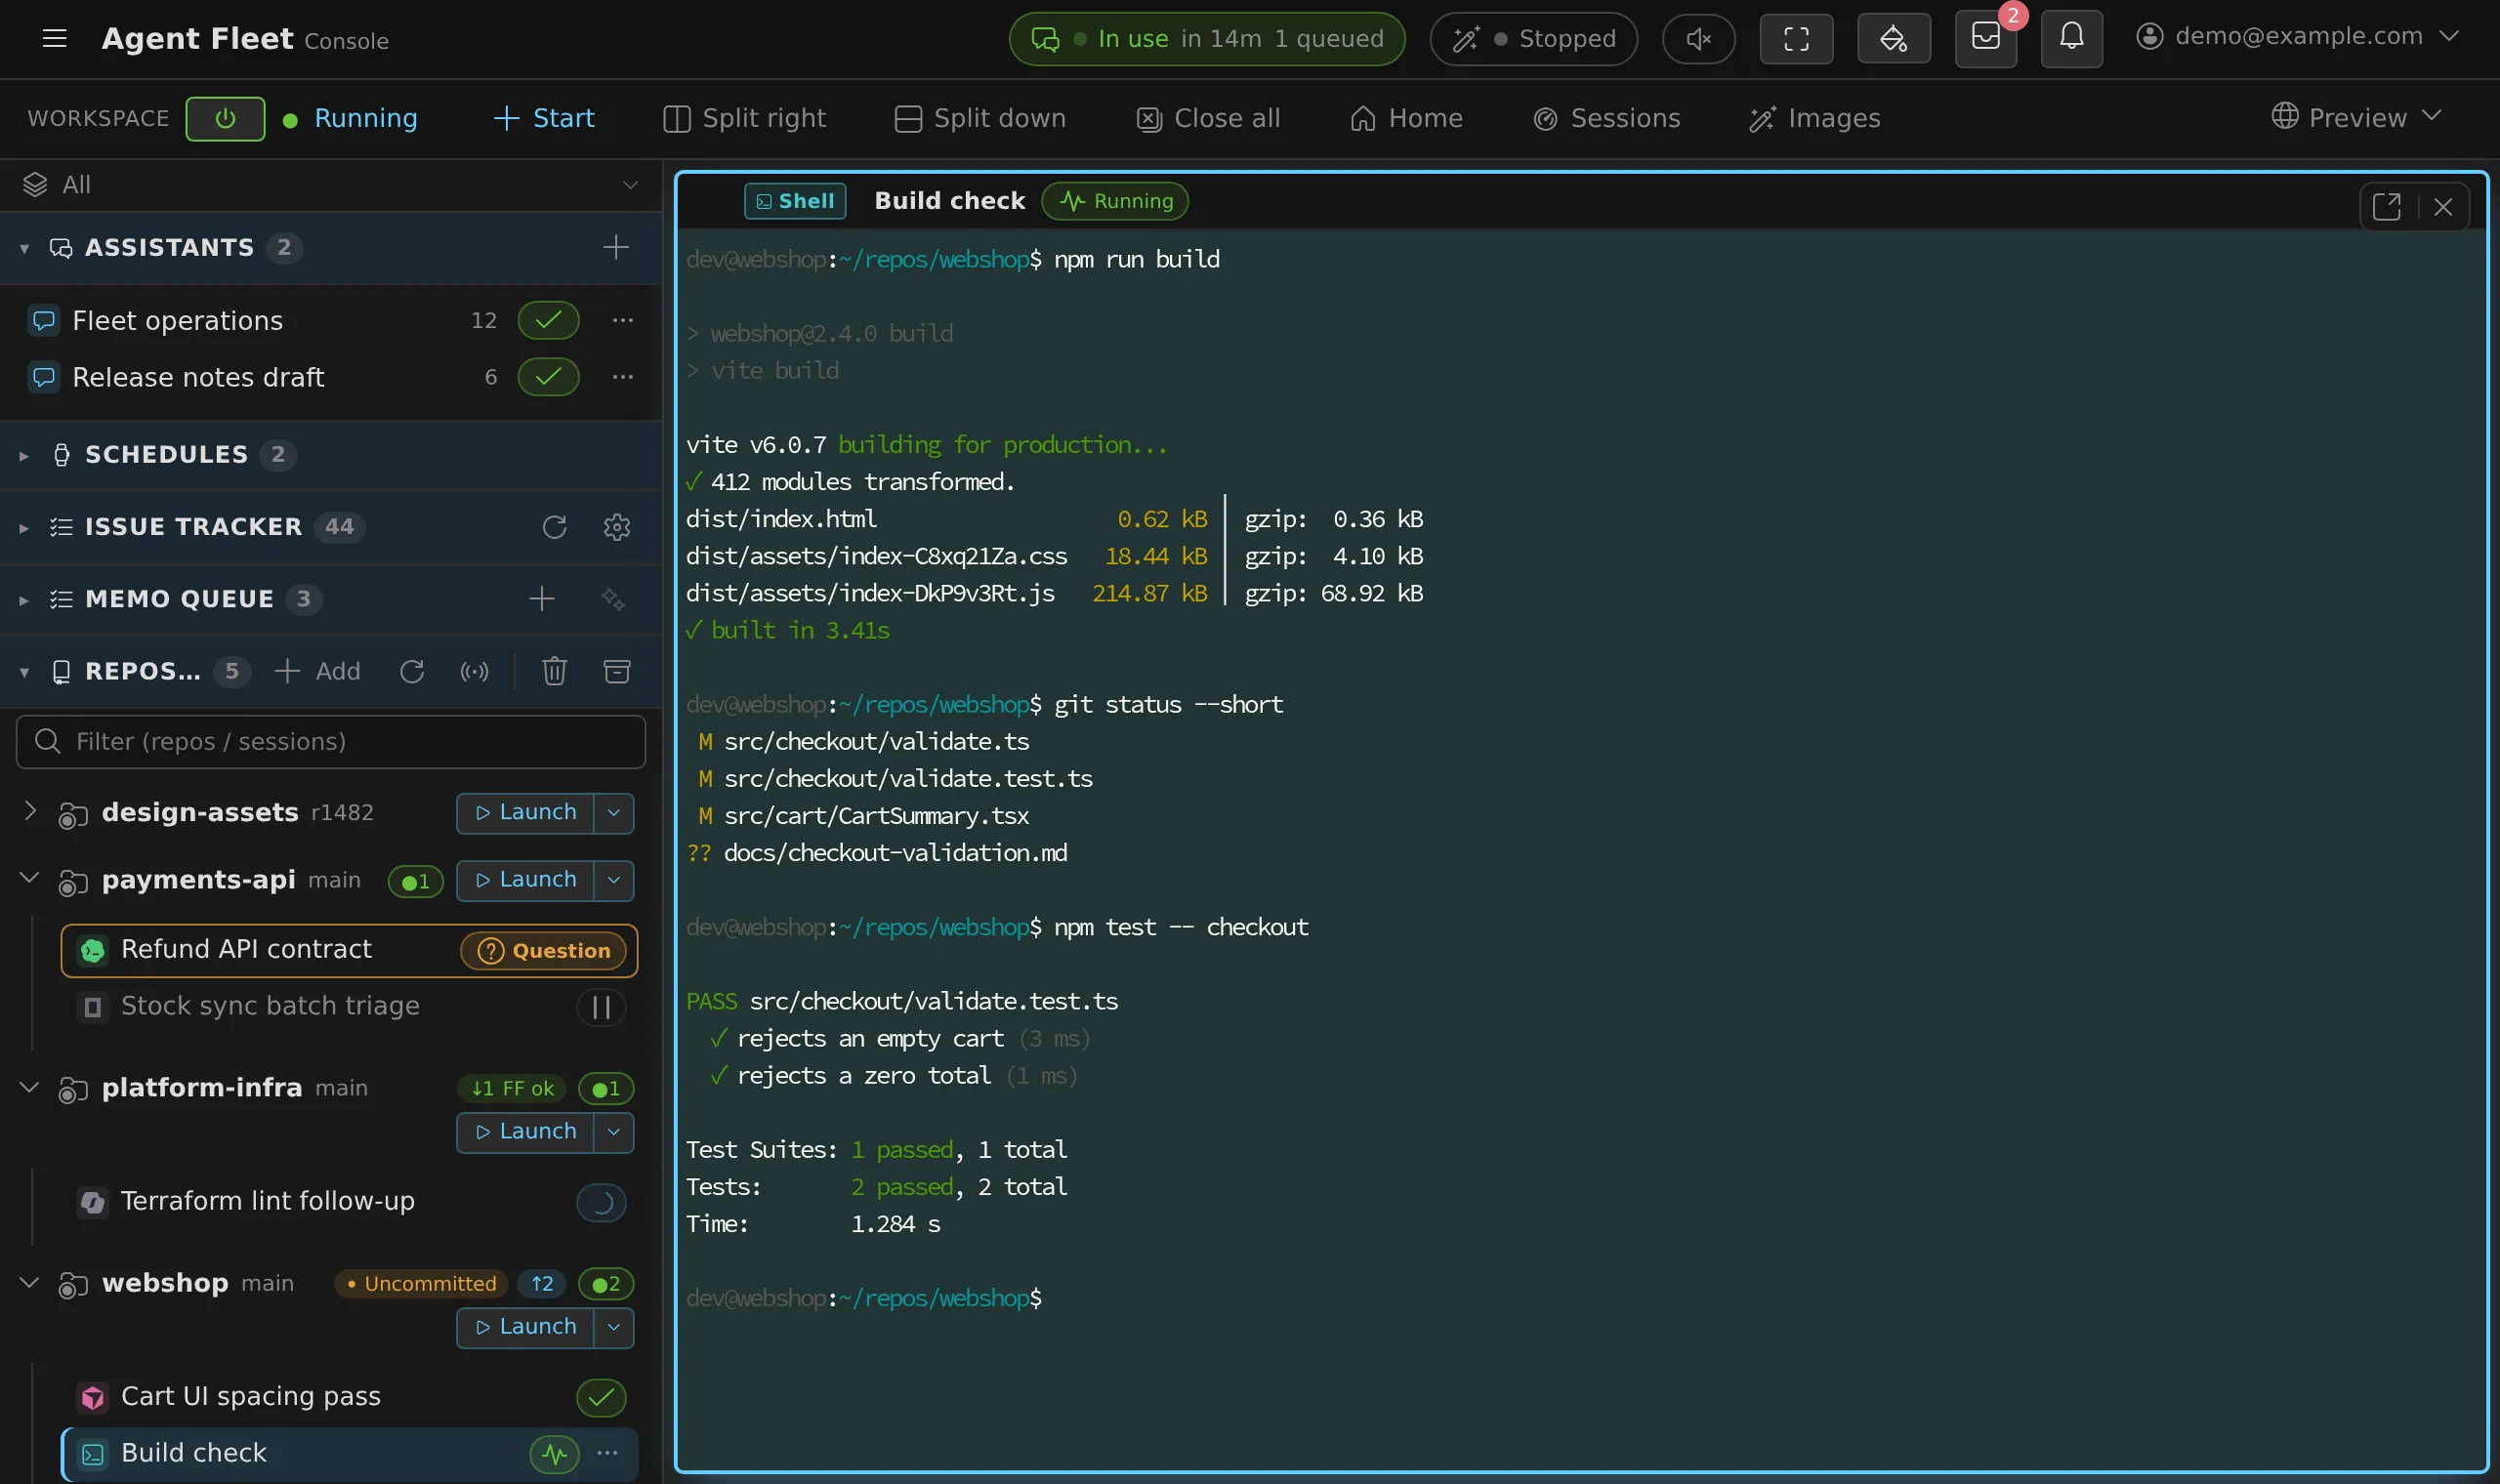
Sessions of different agent kinds run side by side, each in its own worktree. One view shows which sessions are working and which wait on a question, a plan or a permission prompt, and colours the ones waiting on you so they stand out.
Follow and steer from the browser
Every session is mirrored live. Questions, plans and permission prompts arrive as cards you answer in place.
- Or answer from the session's Discord / Slack thread, with buttons.
- The Console works in a phone's browser.
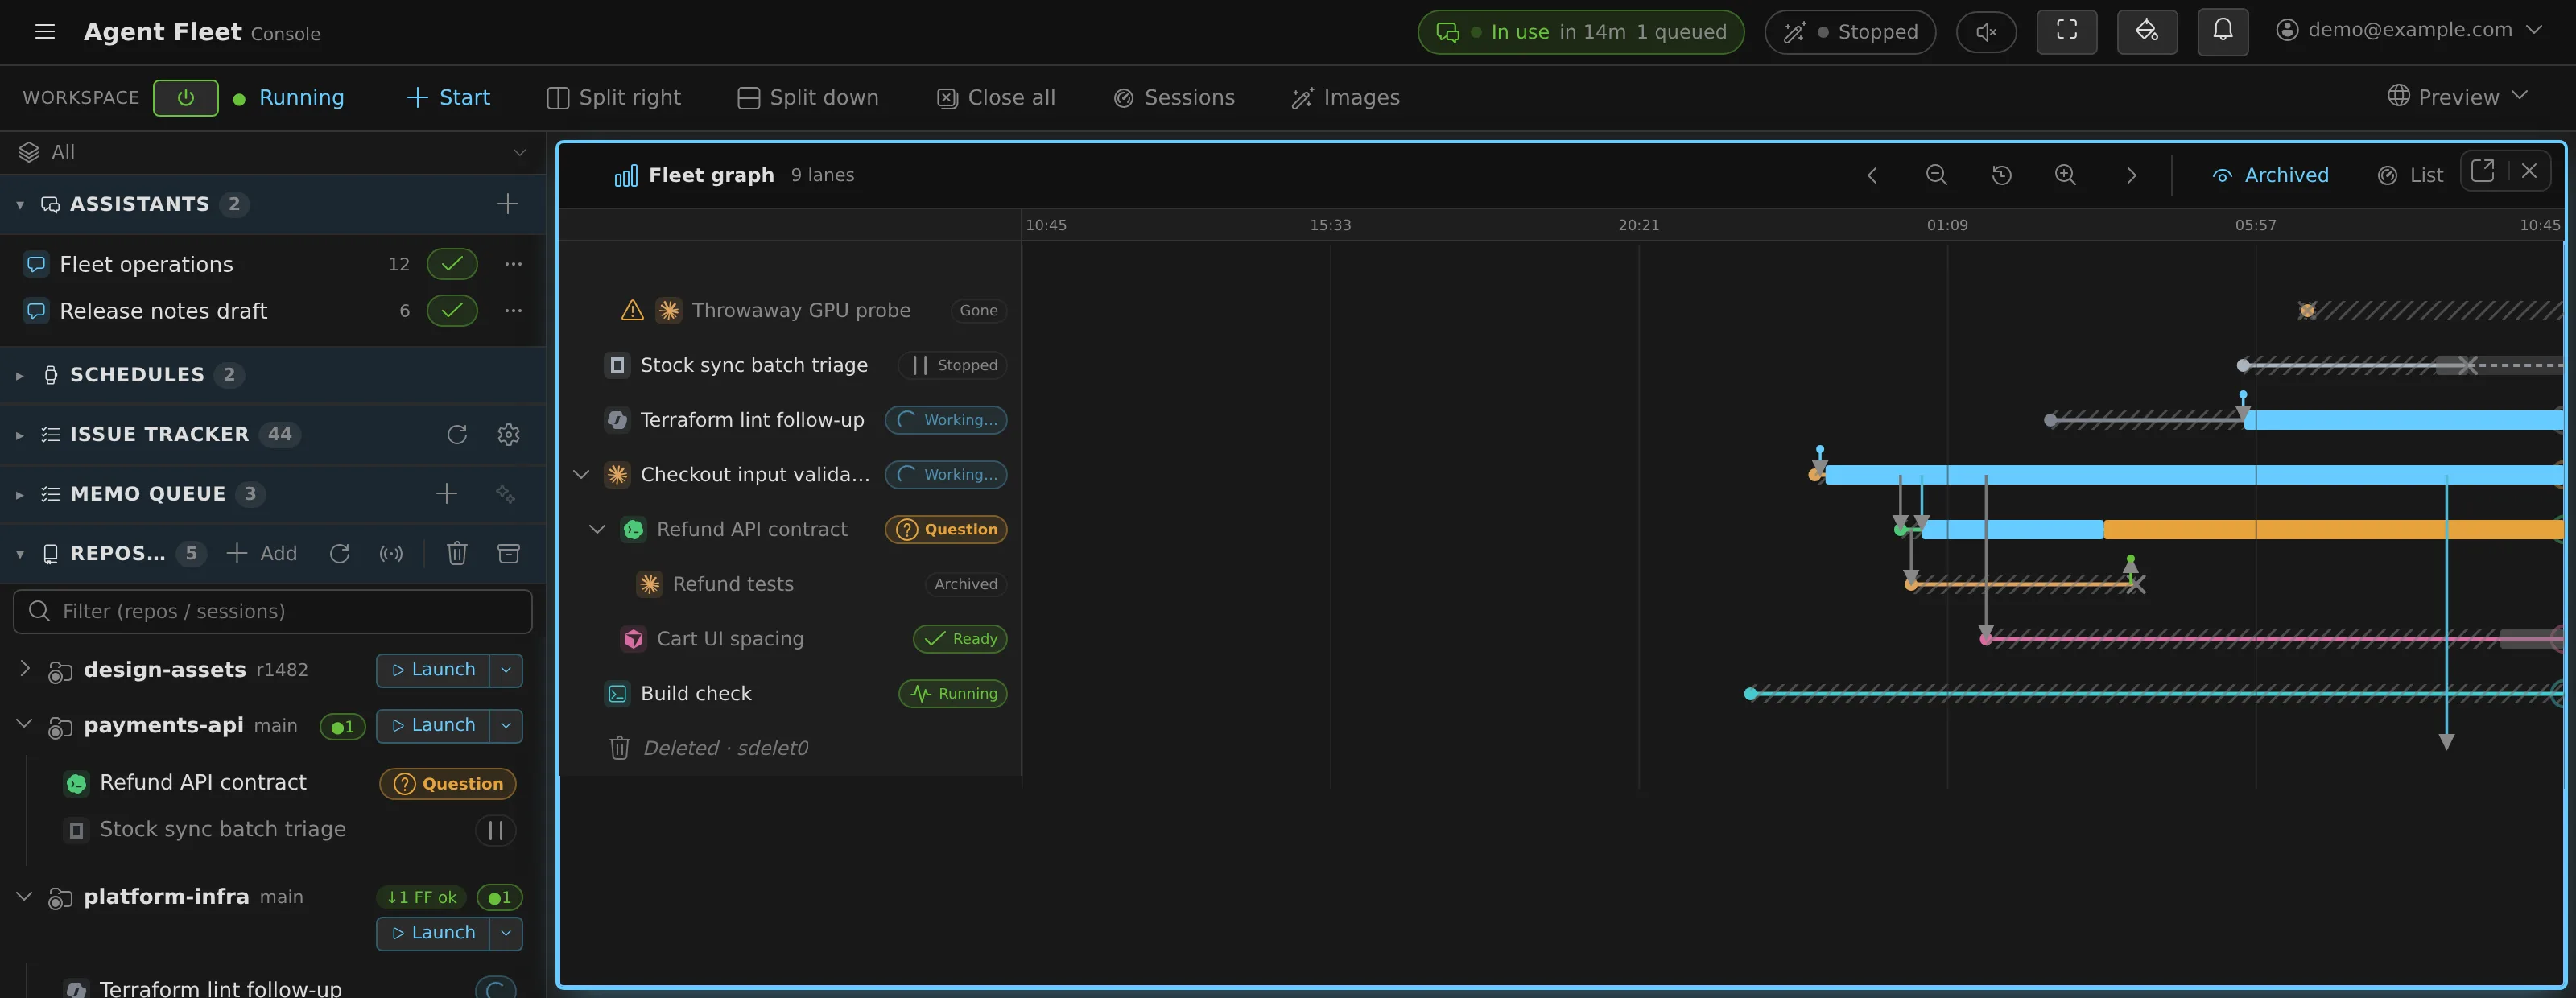
Sessions that start sessions
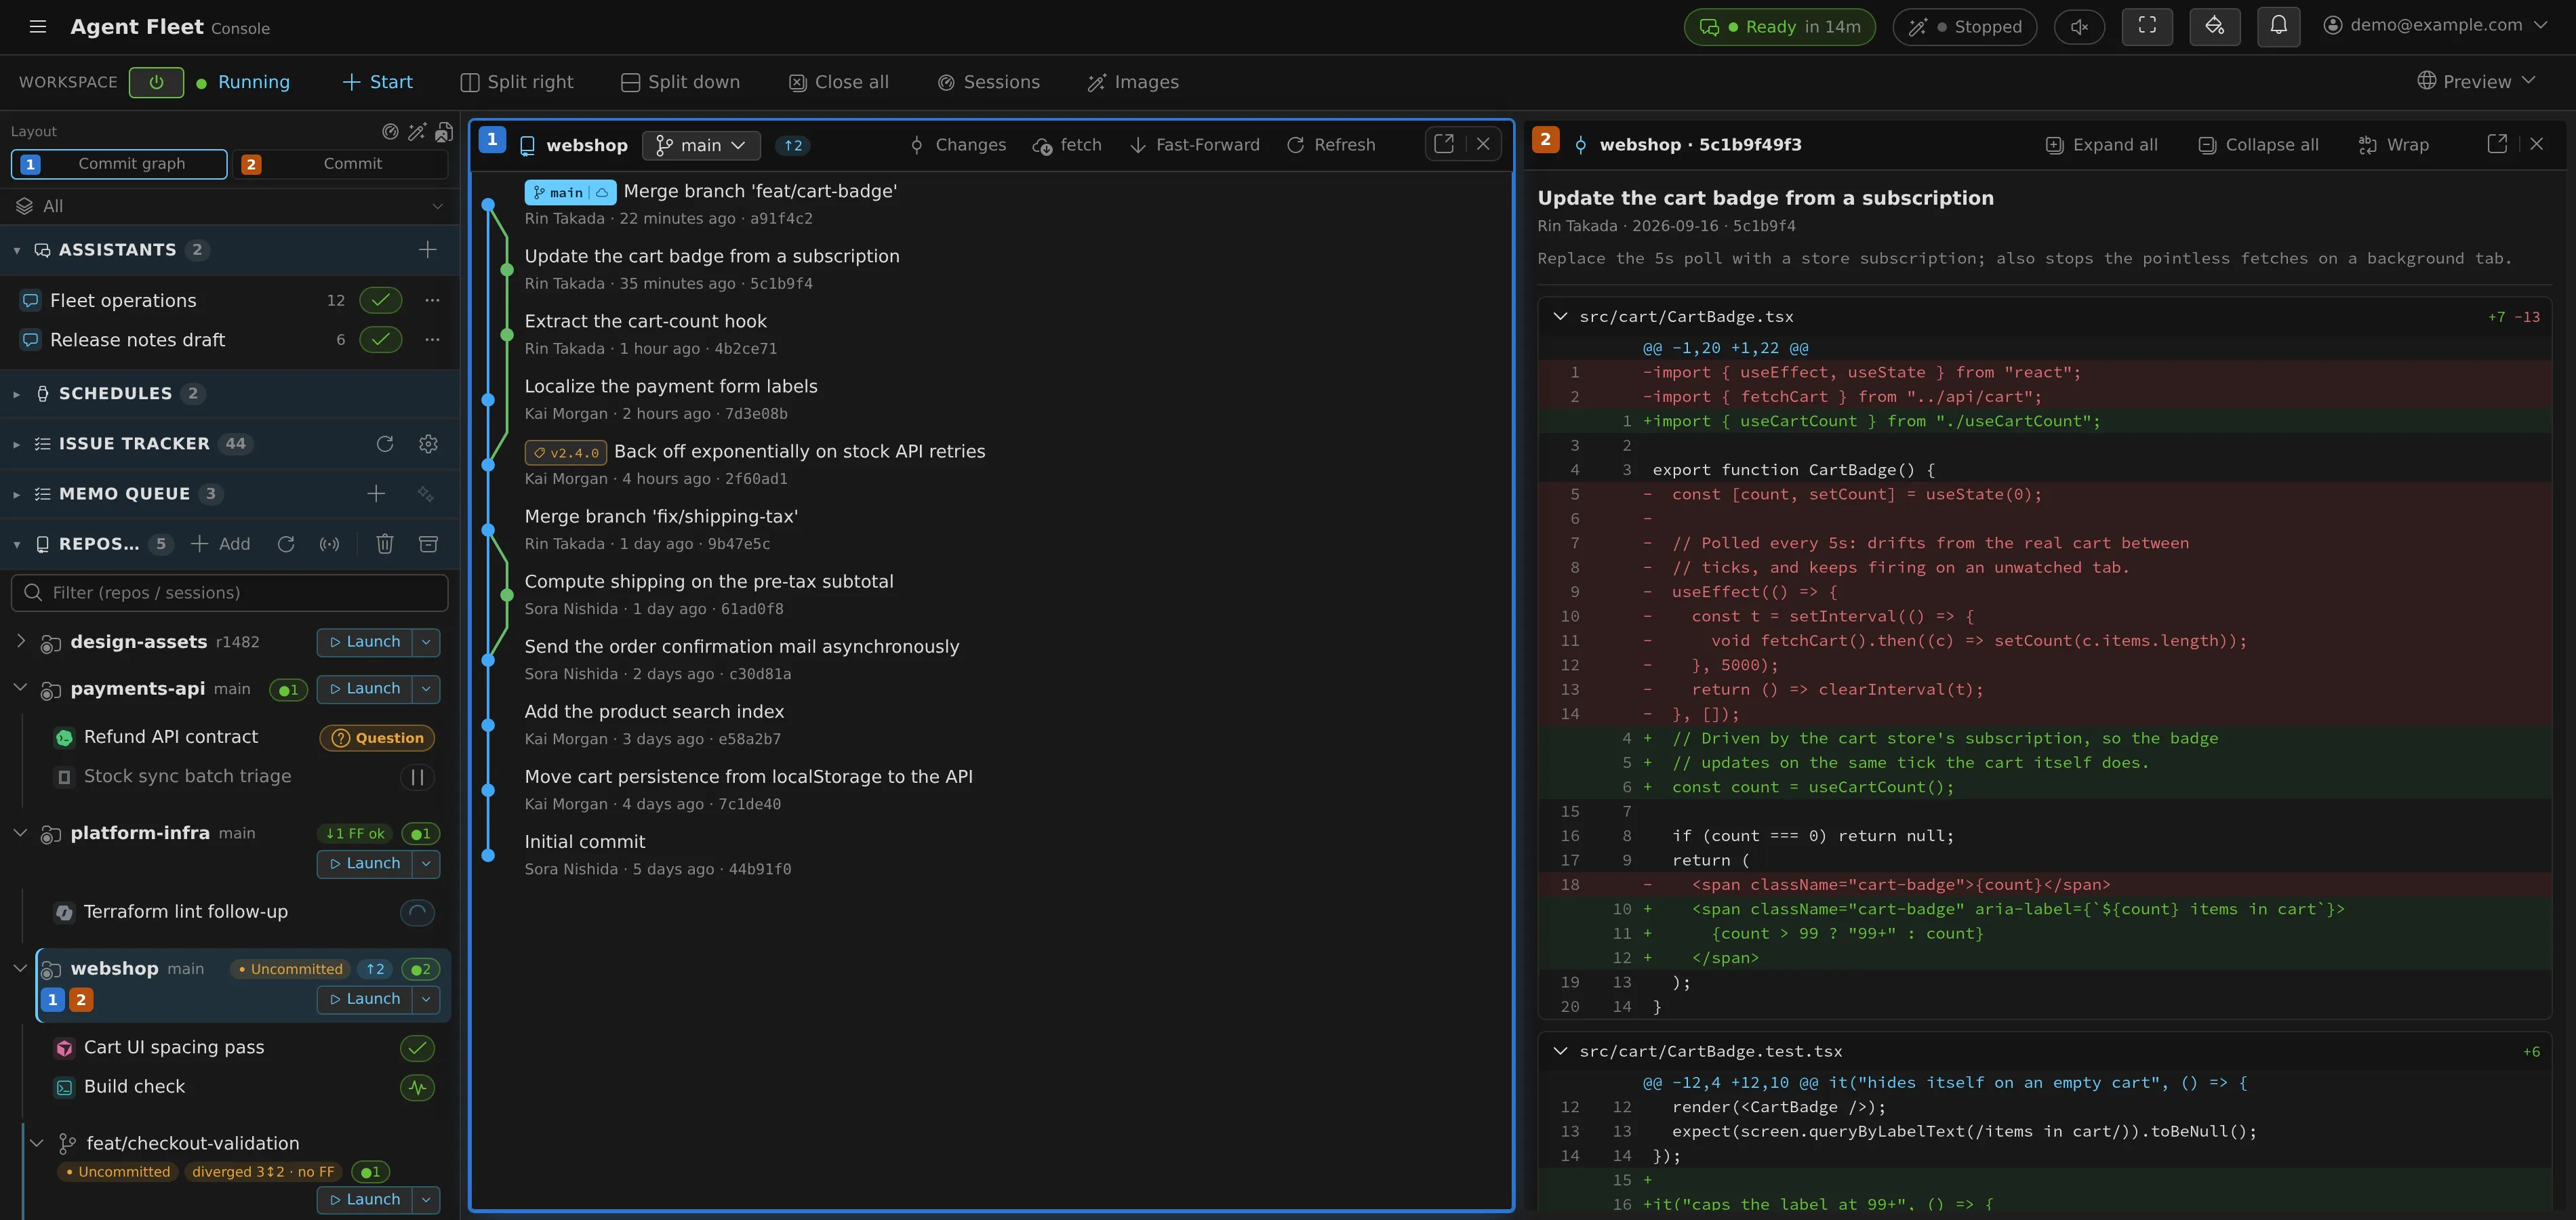
A session can hand a review to another agent kind and get one report back, or move its whole job to another kind when its usage limit runs out. The fleet graph draws who started whom, what passed between them, and when each one was working.
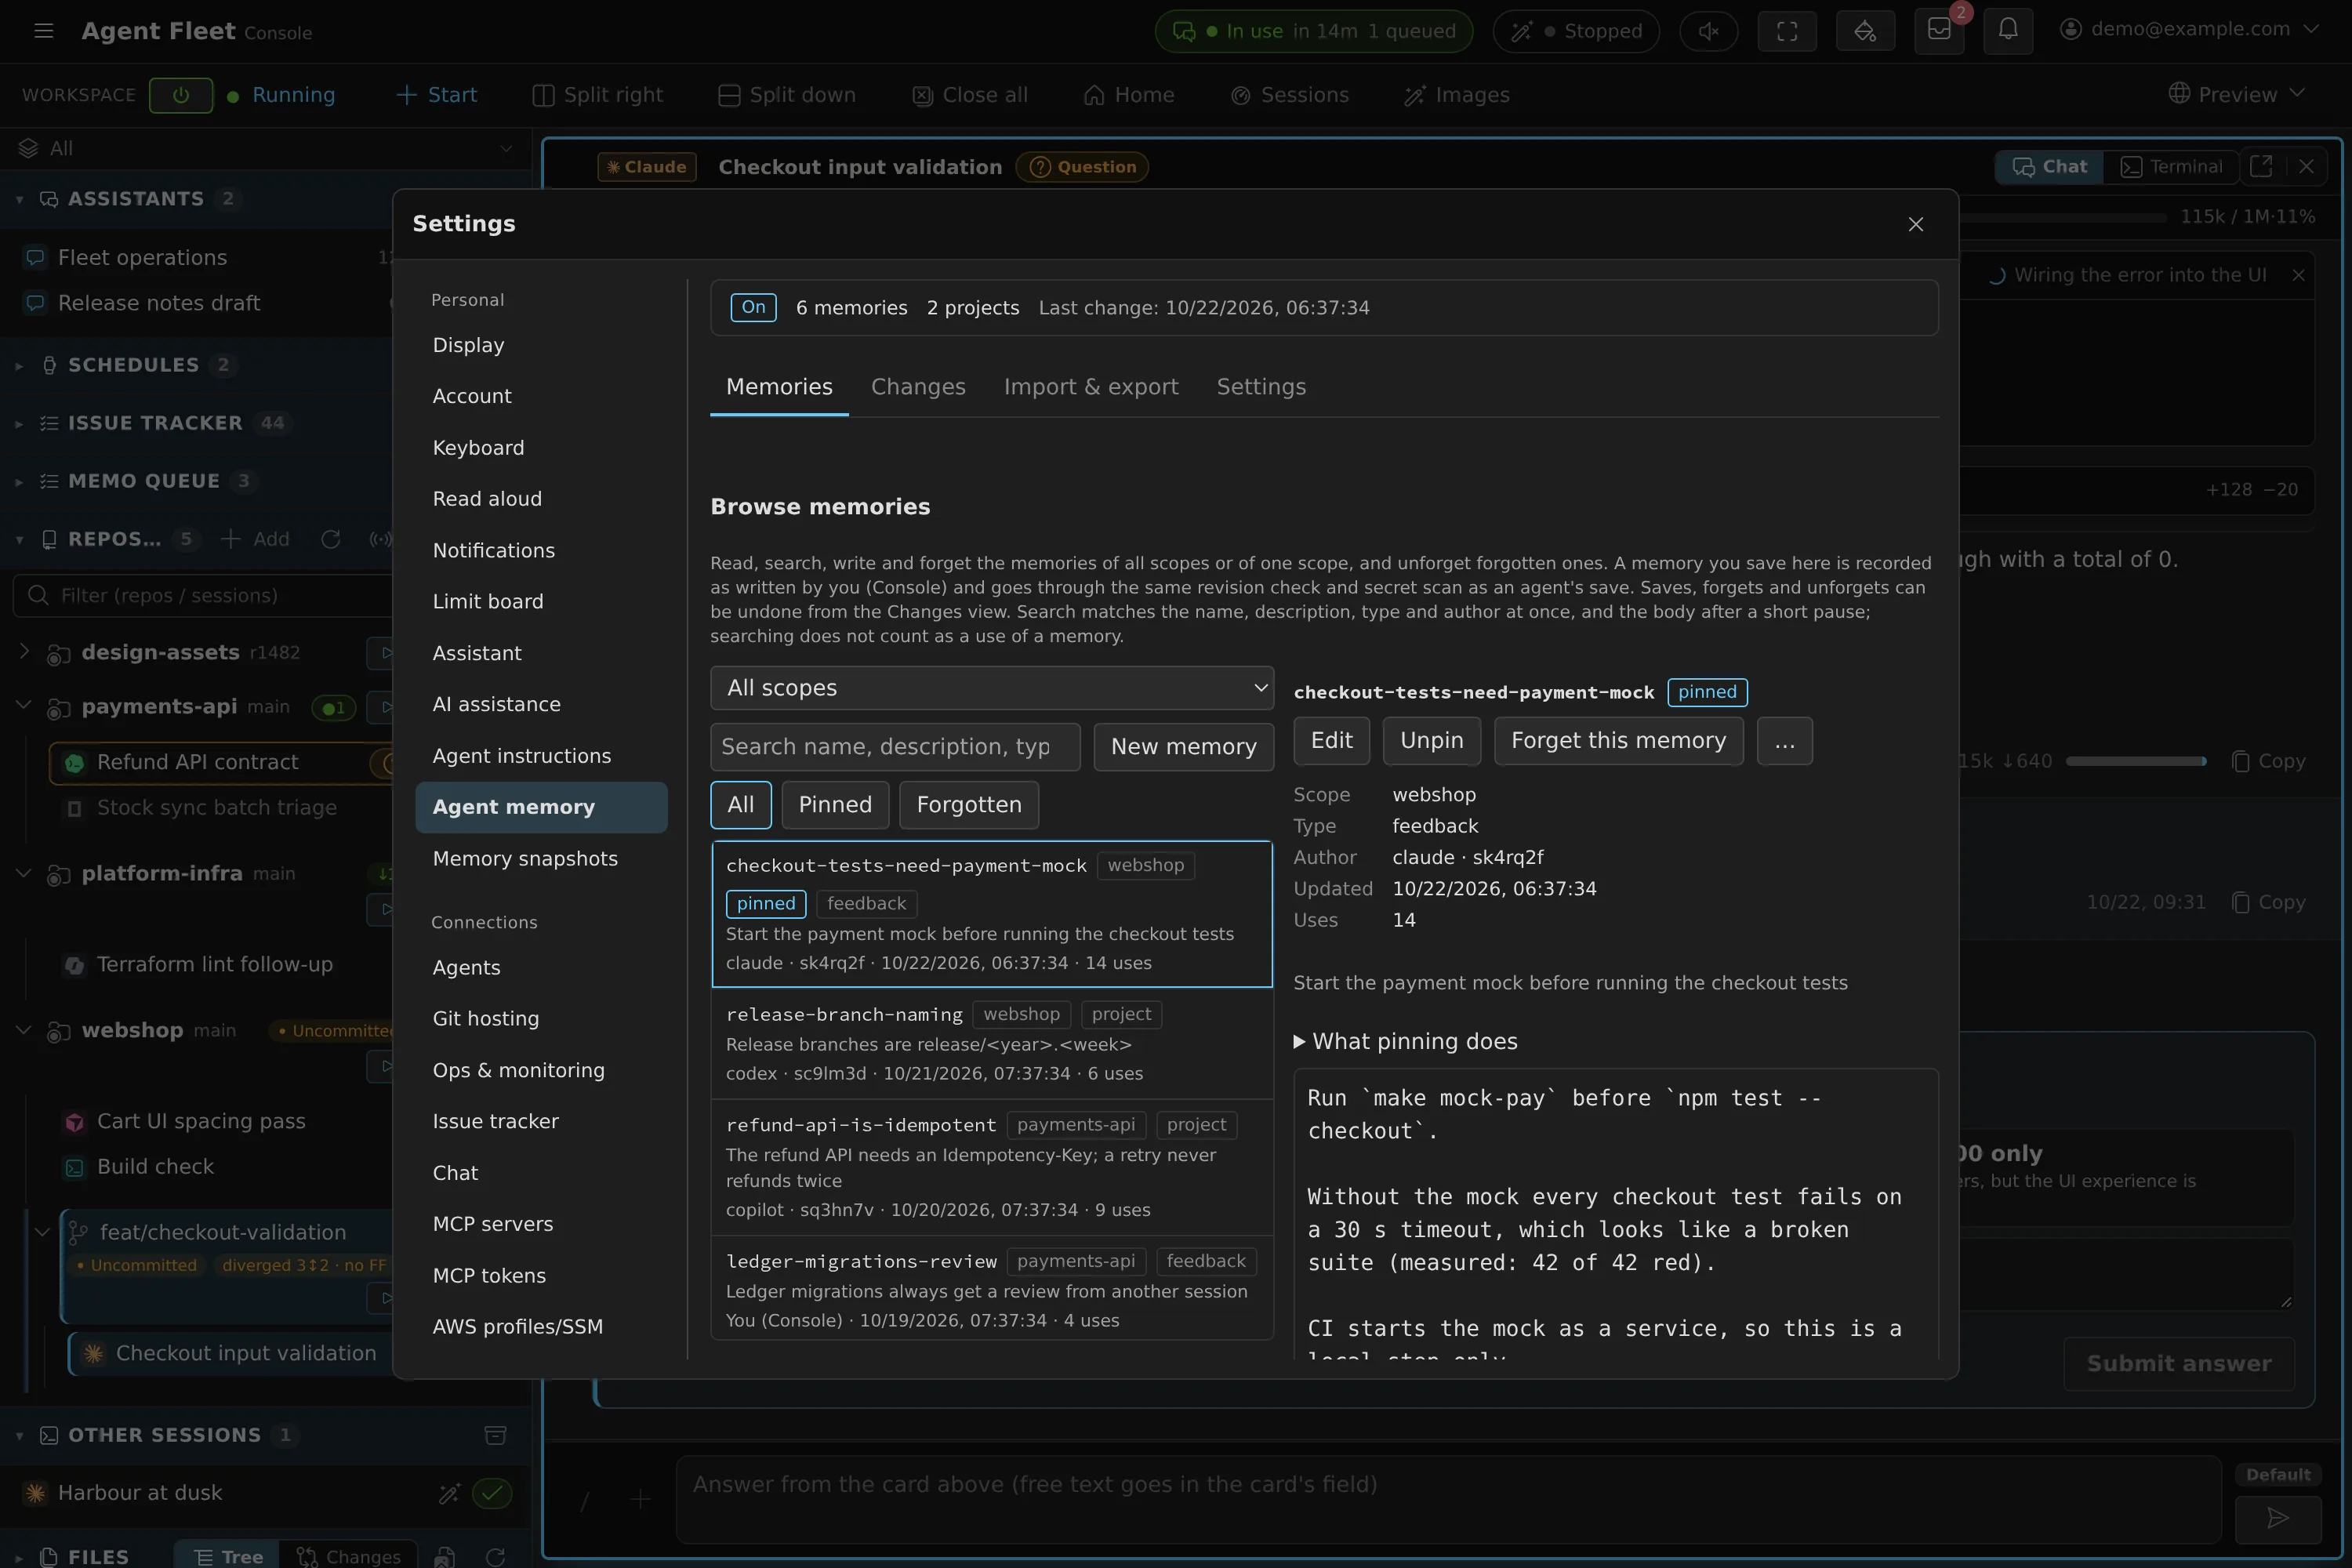
One memory, every agent
With Agent memory on, what one session saves is read by the next session of any kind. Every change records the agent and session that made it, and you can edit, pin, forget or revert it from the Console.
- It is off by default, and each member turns it on.
- Your own Claude Code, Claude Desktop or claude.ai can use it too.
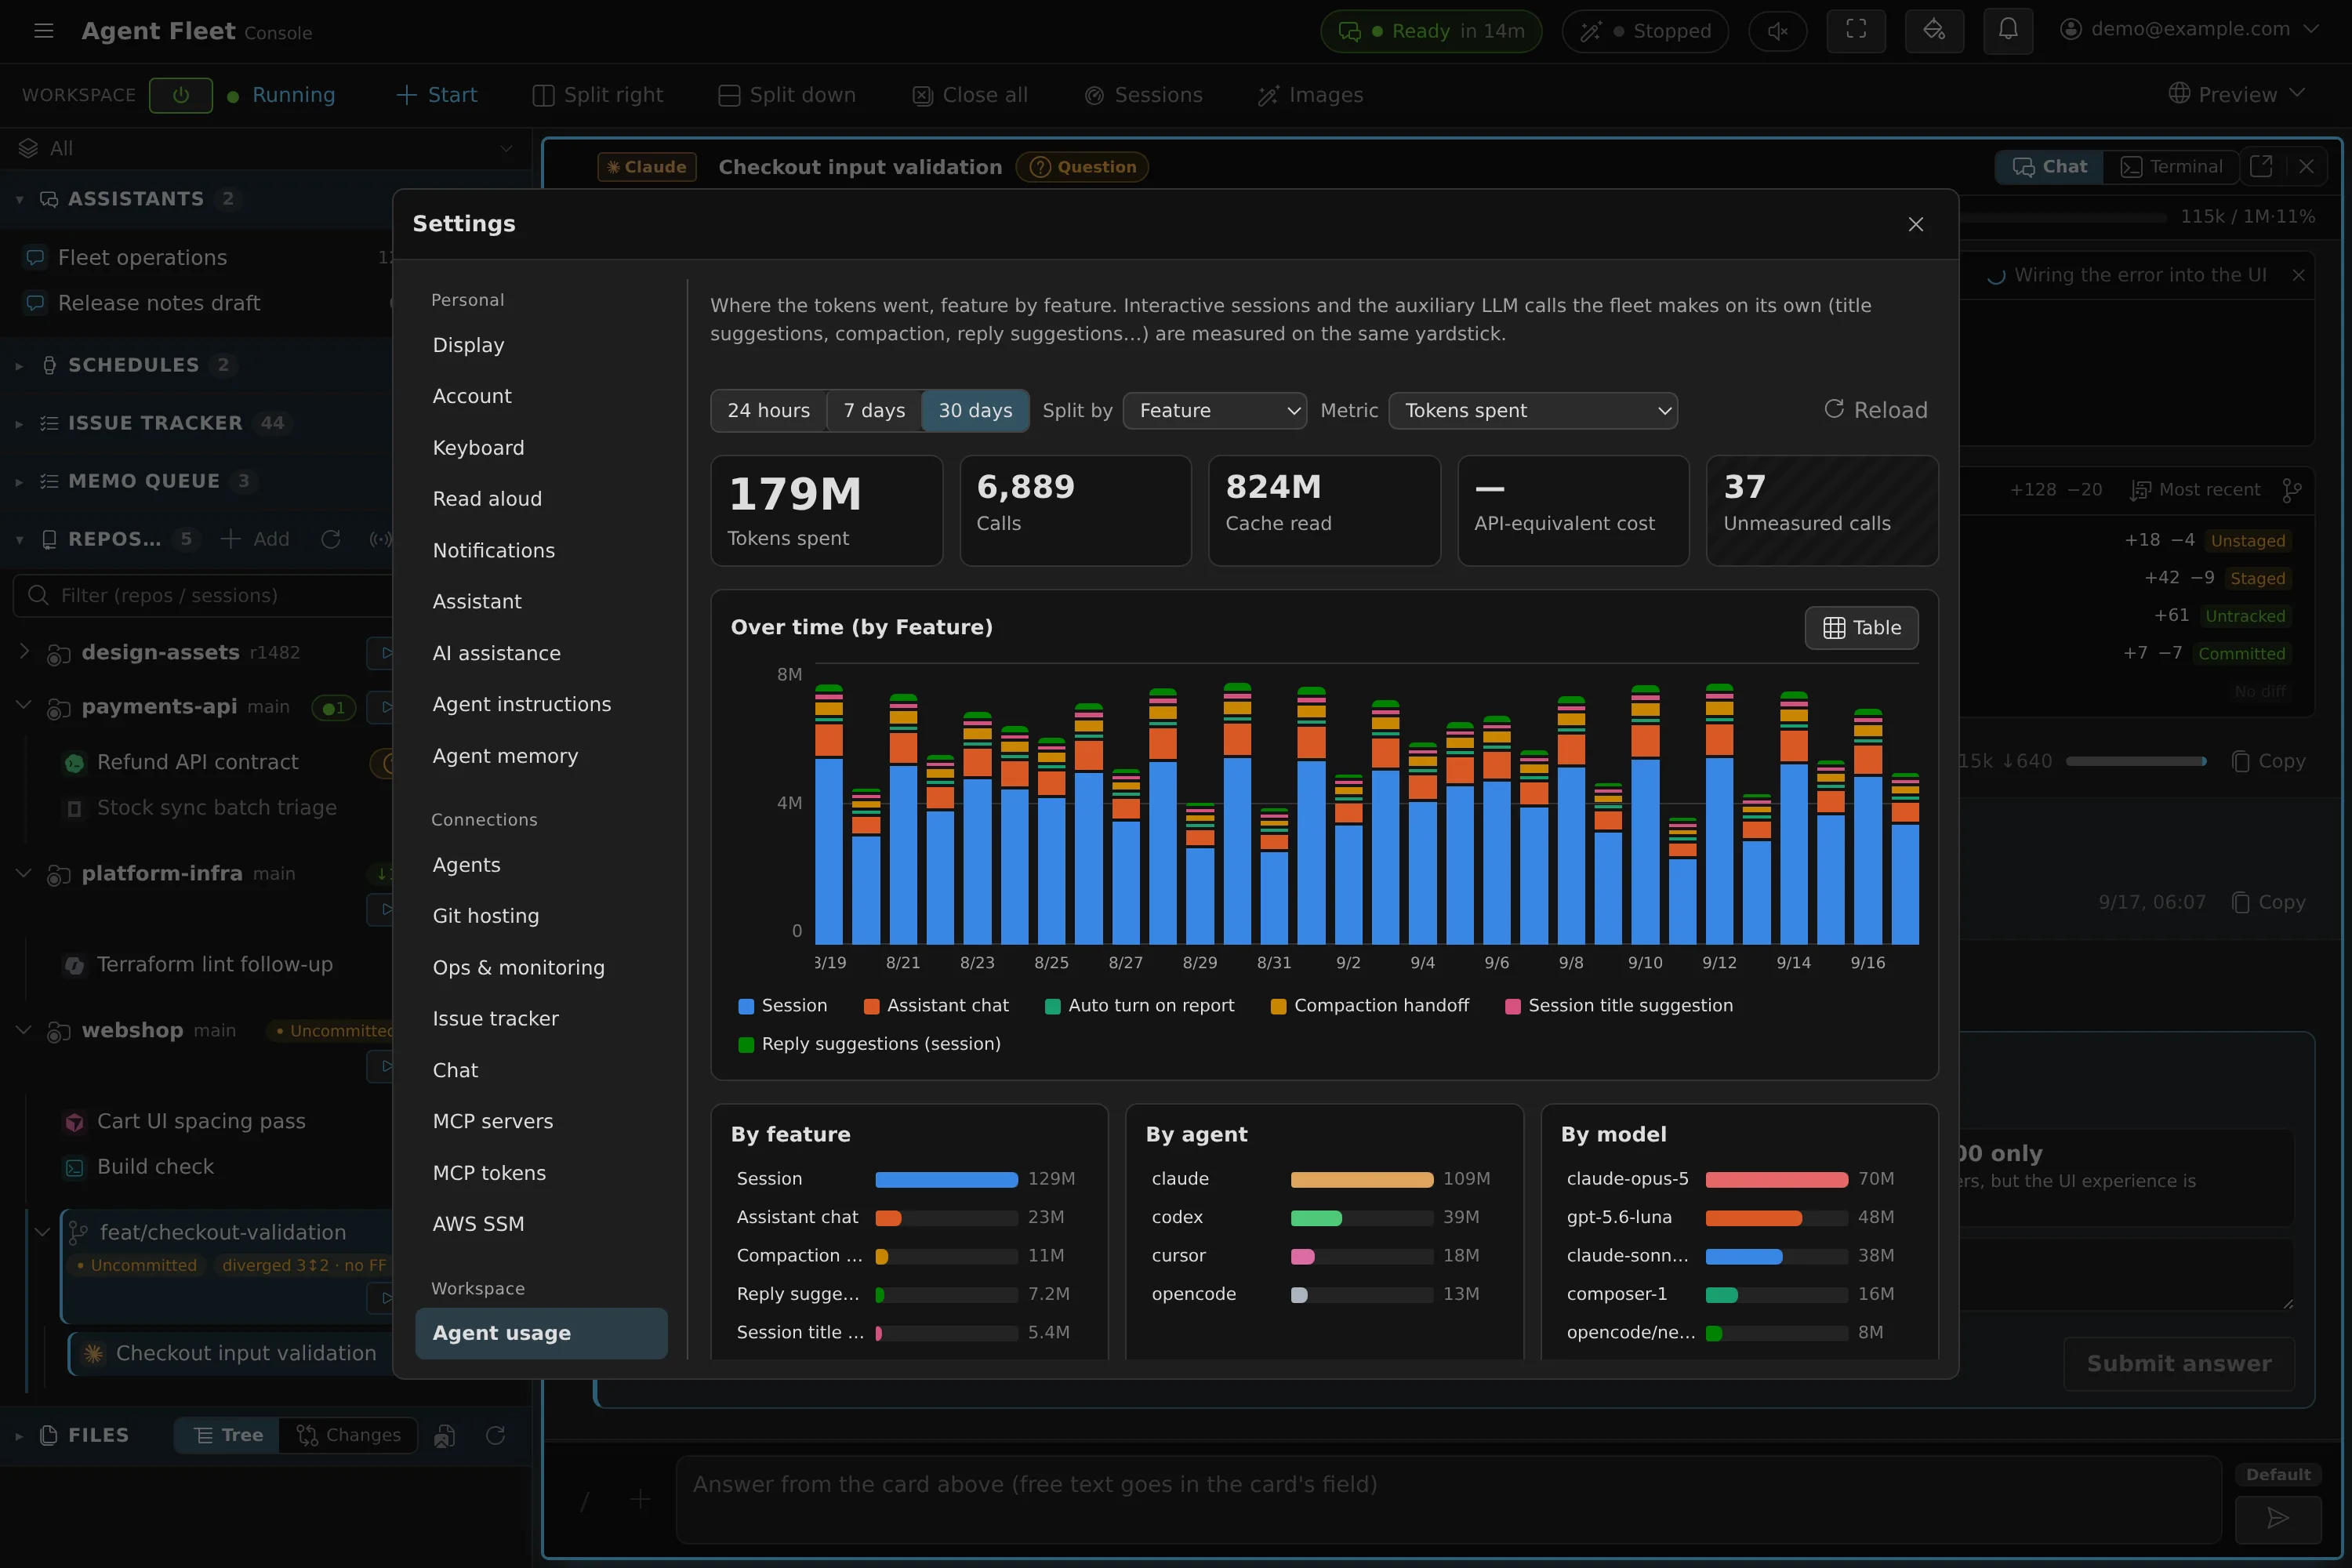
One yardstick for spend
Token use is broken down by feature, agent and model, over 24 hours, 7 days or 30 days. Calls that report no tokens are counted as unmeasured, never as free.
Unattended work
Scheduled runs wake a stopped workspace and run the prompt. A Claude Code, Muse Code or Managed Codex turn cut short by a usage limit resumes when the limit lifts. Any other session can move to an agent that still has quota, so nothing sits dead until morning.
Rules that reach every agent
Fleet-wide policy and per-member instructions reach each agent kind in its CLI's own idiom; Cursor is the one kind that takes neither. The memories Claude Code and Codex build up on their own are snapshotted and can be rolled back.
Upstream changes
Built to survive upstream changes
Agent CLIs change every few days. Supporting nine of them is only worth something if the support keeps working.
Pinned
Every CLI is pinned to a version that was verified. Self-update is opt-in.
Tested against the real CLI
A daily watcher notices when a CLI publishes a new version and dispatches a contract test that drives the real CLI, its interactive TUI included, against what Agent Fleet depends on.
Seen is not tested
"We saw a new version" and "we tested it" are recorded separately, so a release that has not passed its contract is never mistaken for one that has.
Security
Self-hosted, by design
One company runs one deployment, on its own infrastructure. Companies are isolated by separate deployments, not by boundaries inside a shared service.
Your infrastructure
A single Linux host with Docker Compose, AWS, or Google Cloud on GKE (a preview), or an Apple Silicon Mac for one user. The same core everywhere.
Isolated workspaces
Each member gets a persistent container with cgroup CPU and memory quotas and per-user network isolation. The Docker-less native edition uses a bubblewrap sandbox instead.
Your identity provider
Sign in with Google, Microsoft Entra ID, Okta, any OIDC provider or a GitHub organization. It supports tenants, with member, tenant administrator and deployment administrator roles.
Your own seats
Each member signs in to the agent CLIs with their own account. The deployment neither bundles nor shares AI-provider credentials.
Outbound traffic on record
On AWS, an optional egress gateway (a preview) sends workspace web traffic out through one address, records each connection with its workspace, and can enforce an allowlist. It drops other traffic, such as git over SSH. Choosing the egress route
An audit trail
Operations that change or destroy something are written to the tenant's audit log, with who did them. Terminal input and output are not stored.
Encrypted secrets
Credentials are stored with envelope encryption: per-workspace keys wrapped by a tenant key.
Auditable, and candid
The source is Apache-2.0. The security policy documents the threat model and the residual risks an operator should understand.
Editions
Choose where it runs
Start on one Linux host. Move to AWS when you need task-level isolation, and change your mind later if you want. Google Cloud is in preview.
compose
For a team, on one Linux host with Docker, with automatic TLS and sign-in through your identity provider.
native
A single user on WSL2 or a personal Linux box. Installs into your home directory.
Apple Silicon
For one user: the compose edition on Docker Desktop, OrbStack or colima, or the native package inside a Linux VM (Lima, an OrbStack machine). Intel Macs and team deployments on a Mac are not covered.
ec2-single
Compose on one AWS VM, operated the same way as on your own host.
ecs · ecs-ec2
Task-level isolation, per-user fault isolation and rolling image replacement.
kubernetes · GKE
It runs on a GKE Standard cluster but is not supported for production yet: homes have no backup, and there are no browser features or per-member cost.
Choosing a deployment target, costs included →
Try it on your own machine
The native edition needs Linux on x86_64 or arm64, WSL2, or a Linux VM on an Apple Silicon Mac, and no Docker. On a Mac you can also run the Compose edition on Docker Desktop, OrbStack or colima, for one user. Each member signs in to the agent CLIs with their own account from the Console.
Installer details · Setting up compose for a team · Mac (Apple Silicon)
curl -fsSL https://raw.githubusercontent.com/k-k1/agent-fleet-dist/main/install.sh | bash
af start
# then open http://localhost:8099